Businesses in One-North rely on websites, applications, cloud platforms, and connected networks to manage daily operations. These systems also hold valuable business information, customer records, and intellectual property. A single security gap can expose this information and affect business continuity.
Global Quality Services offers VAPT services in One-North, Singapore, to help businesses identify vulnerabilities, assess security risks, and strengthen their IT environments. The need for regular security testing has become more urgent. According to Singapore’s Cyber Security Agency (CSA), almost nine in ten organizations surveyed experienced at least one cybersecurity incident in 2025, as reported in its October 2026 Cybersecurity Health Report.
Our consultants help businesses understand their security requirements and plan suitable assessments. Explore our VAPT services and see how Global Quality Services can support your cybersecurity goals.
Why Do Businesses in One-North Need VAPT Services
One-North hosts technology companies, research centers, startups, biotechnology firms, and professional service organizations. Many of these businesses manage sensitive information and depend on digital platforms for daily operations. Vulnerability Assessment and Penetration Testing (VAPT) helps organizations find security weaknesses before attackers exploit them. Businesses in One-North can use VAPT to:
- Identify vulnerabilities across networks, applications, and IT infrastructure.
- Protect confidential business information and customer data.
- Detect weak access controls and insecure configurations.
- Assess exposure to common cyberattacks.
- Reduce security risks across cloud and digital platforms.
- Strengthen cybersecurity controls before client assessments and audits.
- Support information security and compliance objectives.
Our VAPT Services in One-North, Singapore
Global Quality Services helps businesses identify their testing requirements and select suitable VAPT services based on their IT environment. Our service coverage includes the following areas.
1. Network Penetration Testing
We assess internal and external networks to identify exposed services, weak configurations, access control gaps, and potential entry points. This helps your IT team understand how attackers could target your network.
2. Web Application Penetration Testing
We examine websites, customer portals, and business applications for security flaws. Testing covers authentication, session management, access controls, input validation, and common application vulnerabilities.
3. Mobile Application Penetration Testing
We assess Android and iOS applications for weaknesses in data storage, application permissions, authentication, and communication security. This helps businesses protect user information and mobile services.
4. Cloud Security Assessment
We review cloud environments for insecure configurations, exposed storage, excessive user permissions, and access control weaknesses. The assessment helps businesses improve the security of their cloud infrastructure.
5. Vulnerability Assessment
We examine IT systems, servers, networks, and software to identify known vulnerabilities, outdated components, and configuration issues. The results help your team prioritize security improvements.
6. API Security Testing
We assess APIs that connect websites, applications, and business platforms. Testing focuses on authentication flaws, broken access controls, excessive data exposure, and insecure API configurations.
7. Wireless Network Security Testing
We examine wireless networks for weak encryption, insecure access points, unauthorized connections, and configuration gaps that could expose business systems.
What Will Your Business Get from a VAPT Assessment
A VAPT assessment should give your business a clear picture of its security weaknesses. It should also help your IT team decide which issues need immediate attention. The assessment report should cover:
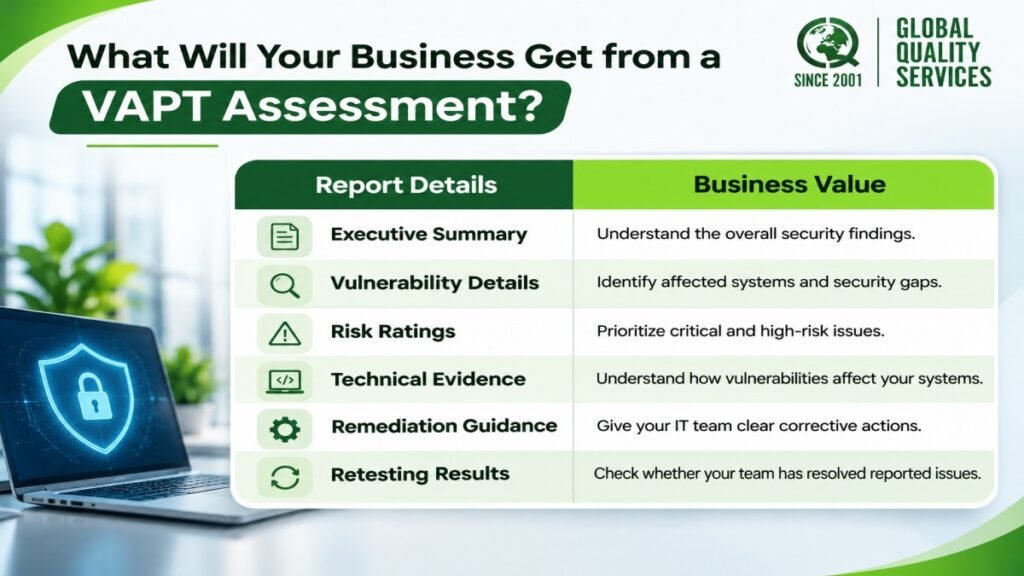
These findings help management prioritize security improvements and allocate resources where they matter most.
Which Businesses in One-North Need VAPT?
VAPT benefits businesses that handle sensitive information, operate digital platforms, or depend on connected IT systems.
- Technology and Software Companies: Protect software products, business applications, APIs, and development environments.
- Biotechnology and Life Sciences Firms: Safeguard research data, intellectual property, and connected laboratory systems.
- Research Organizations: Identify vulnerabilities across databases, research platforms, and shared networks.
- Fintech Startups: Protect financial information, customer accounts, and digital payment platforms.
- Professional Service Firms: Secure client records, internal documents, and business applications.
- Educational Institutions: Assess online learning platforms, internal networks, and connected systems.
When Should You Conduct VAPT?
Regular security testing helps businesses identify weaknesses when their IT environments change. Consider a VAPT assessment:
- Before launching a new website or business application.
- After major network or infrastructure changes.
- When introducing new cloud platforms or APIs.
- Before a client security assessment or compliance audit.
- After fixing critical security vulnerabilities.
- When expanding your IT infrastructure.
- As part of your regular cybersecurity review.
VAPT and ISO 27001: Supporting Better Information Security
VAPT and ISO/IEC 27001 address different aspects of information security. VAPT identifies technical weaknesses in IT systems, while ISO 27001 helps organizations establish an Information Security Management System (ISMS).
Businesses in One-North can use VAPT findings to review technical risks and improve relevant security controls within their information security program.
However, VAPT alone does not establish ISO 27001 compliance. Organizations must also address the standard’s risk management, operational, documentation, and management requirements.
How Does Our VAPT Engagement Work
Global Quality Services aligns the consulting engagement with your business requirements and assessment scope.
Step 1: Requirement Discussion
We discuss your business objectives, IT environment, and security testing requirements.
Step 2: Scope Definition
We identify the applications, networks, systems, and infrastructure that require assessment.
Step 3: Security Assessment
The agreed testing team examines the defined environment and identifies security weaknesses.
Step 4: Findings and Recommendations
You receive assessment findings, risk classifications, supporting evidence, and recommendations for corrective action.
Step 5: Remediation Review
We help your team understand the findings and plan improvements. You can also arrange retesting to verify the fixes.
Why Choose Global Quality Services for VAPT Consulting in One-North
Choosing a reputed consultant helps your business connect security requirements with practical business objectives. Global Quality Services brings an established management consulting background and experience across international certification and compliance requirements. Here is what distinguishes our consulting practice:
- 26 years of management consulting experience.
- 1,450 customers served across different industries.
- Business presence across 17 locations.
- Experience delivering 1,200 training sessions.
- Singapore-based consulting operations.
- Expertise in ISO 27001, SOC 2, PCI DSS, and international compliance requirements.
- SCMC-certified management consulting background.
- Business-focused consulting
Our experience with information security and compliance requirements helps us understand the wider security objectives behind a VAPT engagement. We focus on clear communication, relevant assessment requirements, and practical recommendations that support business decisions.
Secure Your Business with VAPT Services in One-North, Singapore
Unidentified security weaknesses can put your business data, applications, and operations at risk. Work with Global Quality Services to understand your VAPT requirements and identify the right assessment scope for your organization.
Contact Global Quality Services today to discuss your network, application, or cloud security testing requirements in One-North, Singapore. Our consultants will help you identify suitable assessment options and take a more informed approach to protecting your business.
Frequently Asked Questions
1. Does VAPT cover both internal and internet-facing systems?
Yes. Your assessment can cover internal networks, internet-facing systems, servers, applications, and other agreed IT assets. The final scope depends on your business requirements.
2. Do we need to share administrator credentials for VAPT?
Not always. Some assessments use limited access, while others require authenticated accounts to examine security controls in greater detail. Your testing scope will determine the access requirements.
3. Can VAPT help us meet client cybersecurity requirements?
Yes. VAPT reports can provide evidence of security testing and help your business address specific client requirements. However, the assessment alone does not guarantee compliance with every client or regulatory requirement.
4. Can we test a live production website?
Yes, but your testing team must agree on the scope, access permissions, testing limits, and a suitable time window. These precautions help reduce the risk of service interruptions.
5. Should we test our APIs separately from our website?
Yes, when your APIs handle sensitive information or support important business functions. A separate API assessment can uncover access control and data exposure issues that a standard website review may miss.