Raffles Place is home to businesses that handle confidential customer records, financial information, and other sensitive data. Many rely on cloud platforms to store information, run applications, and serve clients. That convenience also raises an important question: how well do these organizations protect personal data when cloud service providers process it?
The Cyber Security Agency of Singapore reported that 284,300 instances of infected infrastructure were detected in Singapore in 2025, a 142% increase from 2024. This finding highlights the need for businesses to take information security and data protection seriously.
What is ISO 27018 Certification?
ISO/IEC 27018 is an international standard that focuses on protecting personally identifiable information in public cloud environments. It gives cloud service providers guidance on handling personal data when they act as PII processors on behalf of their customers.
The standard addresses privacy practices such as:
- Processing personal information only for agreed purposes
- Controlling access to customer data
- Managing the disclosure and transfer of personal information
- Setting clear data retention and deletion practices
- Supporting transparency around data processing
- Handling security incidents involving personal information
ISO 27018 works alongside ISO 27001. While ISO 27001 addresses information security management more broadly, ISO 27018 adds privacy-focused guidance for public cloud processing. It does not replace ISO 27001 or serve as a standalone information security management system.
Why Do Businesses in Raffles Place Need ISO 27018?
Businesses in Raffles Place often work with customers, financial institutions, technology partners, and service providers across different markets. Many use cloud-based systems to manage business records, customer information, applications, and internal operations.
When a cloud provider processes personal information, customers want clear answers about how that data is handled. They may ask about access permissions, storage locations, data sharing, retention periods, and deletion procedures.
ISO 27018 gives cloud service providers a recognized set of privacy practices to address these concerns. It can be particularly relevant to:
- Cloud service providers and data hosting companies
- SaaS businesses processing customer information
- IT and managed service providers
- Fintech and financial technology companies
- Software development and technology firms
- Organizations offering cloud-based business applications
- Companies processing personal data for overseas clients
For businesses serving enterprise customers, ISO 27018 can also support vendor assessments and privacy-related due diligence. It gives clients a clearer view of how the organization approaches personal data protection.
Key Requirements of ISO 27018
ISO 27018 covers specific privacy practices for public cloud environments. Organizations should understand how these requirements apply to their services, contracts, systems, and daily operations.
1. Consent and purpose of processing
Cloud providers should process personal information according to the customer’s instructions and agreed purposes. They should not use customer data for unrelated activities without the required authorization.
2. Transparency in data processing
Customers should receive clear information about how their personal data is processed. This includes relevant details about data handling, third-party involvement, and changes that may affect their information.
3. Access control and data protection
Organizations should restrict access to personal information based on job responsibilities. They should also use suitable technical and organizational measures to protect data against unauthorized access.
4. Data retention and deletion
Cloud providers should follow agreed retention periods and deletion instructions. They need clear procedures for removing personal information when the service ends or the customer requests deletion.
5. Disclosure and third-party access
Organizations should manage how they share personal information with third parties. They should also communicate relevant disclosure practices and address contractual responsibilities with subprocessors.
6. Security incident management
Cloud providers need procedures for handling incidents that affect personal information. They should define how they identify, report, investigate, and communicate relevant incidents to customers.
7. Privacy-related documentation
Organizations should maintain records that explain their privacy practices and responsibilities. Clear policies, agreements, and operational records help demonstrate how the organization handles personal information.
ISO 27018 Certification Process in Raffles Place
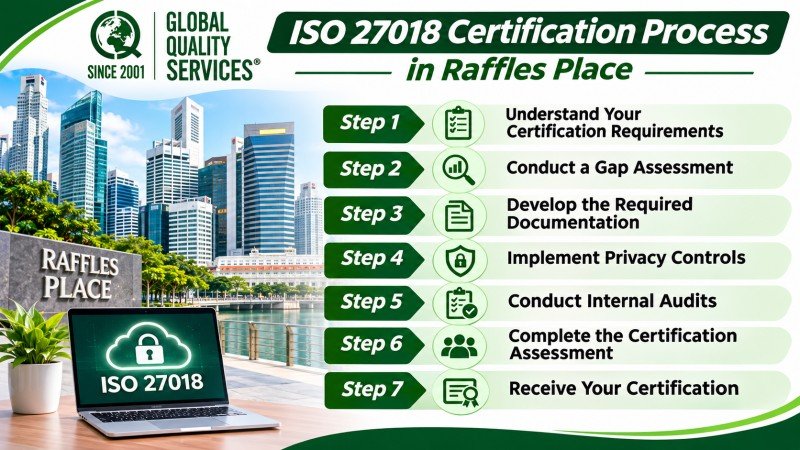
The certification journey requires careful preparation across policies, cloud operations, privacy controls, and employee responsibilities. Global Quality Services can guide your organization through the readiness work and help prepare for the independent certification assessment.
Step 1: Understand Your Certification Requirements
Start by reviewing your cloud services, data processing activities, customer agreements, and privacy responsibilities. This helps define the certification scope and identify the ISO 27018 requirements relevant to your organization.
Step 2: Conduct a Gap Assessment
Compare your existing privacy and information security practices against the applicable ISO 27018 controls. The assessment highlights missing policies, weak procedures, and areas that need attention before the formal audit.
Step 3: Develop the Required Documentation
Prepare the policies, procedures, records, and agreements required for your cloud privacy operations. Documentation should reflect actual business practices rather than rely on generic templates that do not fit your services.
Step 4: Implement Privacy Controls
Put the required controls into practice across relevant systems and teams. Address access permissions, data handling, retention, deletion, disclosure, and incident reporting based on your organization’s operations.
Step 5: Conduct Internal Audits
Review whether employees follow documented procedures and whether the implemented controls work as intended. Record findings, address gaps, and prepare evidence before the external certification assessment.
Step 6: Complete the Certification Assessment
An independent certification body reviews your management system and relevant evidence against the applicable requirements. Your organization may need to address any findings before the certification body makes its decision.
Step 7: Receive Your Certification
Once the certification body confirms that your organization meets the applicable requirements, it can issue the certificate. Continue reviewing your privacy controls and preparing for required surveillance audits.
How Global Quality Services Experts Help You with ISO 27018 Certification in Raffles Place
Choosing the right consultant matters when your organization handles sensitive information across cloud platforms. Global Quality Services is a reputed consultant supporting businesses with ISO certification, management system consulting, training, gap assessments, and audit preparation.
Our Singapore operations offer Singapore Certified Management Consultant expertise and consulting support across information security, privacy, and other management system standards. This broader consulting background helps us understand how ISO 27018 requirements connect with business operations and customer expectations.
Discuss Your ISO 27018 Certification Requirements with Global Quality Services
Are you planning to pursue ISO 27018 certification for your business in Raffles Place? Speak with Global Quality Services about your cloud environment, privacy responsibilities, and certification goals. Our consultants can review your requirements, identify preparation needs, and guide your team through the readiness process. Contact Global Quality Services to discuss your project and take the next step toward ISO 27018 certification.
Frequently Asked Questions
1. Is ISO 27018 certification mandatory for businesses in Raffles Place?
No. Singapore does not generally require ISO 27018 certification by law. However, customers, business partners, or procurement teams may request it as evidence of cloud privacy practices.
2. Can a company pursue ISO 27018 without ISO 27001?
ISO 27018 complements ISO 27001 and is designed to work within its information security management context. Organizations should assess the applicable certification requirements before planning their implementation.
3. Does ISO 27018 apply to SaaS companies?
Yes. SaaS companies that process personally identifiable information in public cloud environments may find ISO 27018 relevant, particularly when they act as processors for customer data.
4. How long does ISO 27018 certification take?
The timeline depends on your existing security controls, cloud infrastructure, documentation, and organizational readiness. A gap assessment can help estimate the work required before the certification audit.
5. Who issues the ISO 27018 certificate?
An independent certification body conducts the formal assessment and makes the certification decision. Global Quality Services supports your organization with consulting, preparation, and audit readiness.