Data breaches always pose risks to corporate reputations, such that mere compliance is insufficient when building customer confidence. Singapore has set new benchmarks in enterprise data governance by codifying the Data Protection Trustmark to become a fully-fledged national standard. Managed under the purview of the Infocomm Media Development Authority, the standard serves as definitive evidence of your auditable data governance controls in accordance with the Personal Data Protection Act.
Official statistics released by the IMDA reveal that over 150 top-tier organizations within Singapore are using certified trustmark frameworks for demonstrative transparency in their data practices. Achieving SS 714:2025 certification puts you ahead in competitive bidding processes, passes rigorous client security audits, and greatly reduces cybersecurity vulnerabilities.
Continue reading below to find out more about how SS 714:2025 certification can safeguard your digital assets, enhance market credibility, and ease your compliance journey.
What is SS 714:2025 Certification
SS 714:2025 is the national data protection standard in Singapore. This means that it offers a standardized process for achieving the IMDA/PDPC Data Protection Trustmark. Organizations receive independent verification that their internal systems for managing data protection align with the requirements of the Personal Data Protection Act.
Being certified under SS 714 allows organizations to prove good practice in handling data, giving them a clear edge over competitors in public sector procurement projects, and reducing risks when undergoing security audits.
Benefits of Getting SS 714:2025 Certification
Meeting this benchmark provides instant business benefits:
- Competitive Edge: Get favored status in government bids and corporate vendor assessments.
- Risk Management: Lower your exposure to regulatory compliance issues and penalties through the Active Enforcement Framework.
- Customer Trust: Demonstrate to clients that you protect their confidential data.
- Efficiency: Develop guidelines on how to collect, safeguard, and dispose of your data internally.
Core Requirements of the Standard
The framework evaluates four primary pillars of data management.
- Governance and Oversight: Appoint a qualified Data Protection Officer and establish clear management policies.
- Data Lifecycle Management: Define strict protocols for consent gathering, secure storage, and safe data disposal.
- Security Controls: Implement strong access restrictions and conduct regular vendor security assessments.
- Individual Rights: Create swift response protocols for consumer inquiries and data correction requests.
Who Should Get DPTM Certified?
DPTM is relevant for any Singapore organisation that collects, uses, or stores personal data. It is particularly valuable for:
- IT and technology companies handling client or user data as part of their service
- Healthcare organisations managing patient records and sensitive health information, which pairs naturally with our HIPAA compliance consultancy
- Financial services firms handling customer financial and identity data
- E-commerce and retail businesses storing customer purchasing and payment information
- HR and recruitment companies managing employee and candidate personal data
- BPO companies processing personal data on behalf of clients, paired with our ISO 27001 certification
- Any organisation bidding for government contracts where data protection capability is a tender requirement
The Four Pillars of the SS 714:2025 Standard
The framework evaluates your entire data handling ecosystem across four primary management pillars:
- Governance and Oversight: Requires appointing a qualified Data Protection Officer, defining executive responsibilities, and maintaining clear operational privacy policies.
- Data Lifecycle Management: Standardizes processes for gathering consent, managing data retention schedules, ensuring secure storage, and facilitating safe disposal.
- Security Controls and Risk Assessment: Directs mandatory Data Protection Impact Assessments, strict access management, third-party vendor reviews, and incident response procedures.
- Individual Rights and Request Workflows: Establishes structured mechanisms to handle customer inquiries, consent withdrawals, data access requests, and correction claims.
How Global Quality Services Facilitates Your SS 714:2025 Certification Journey
Here is a complete process to achieve SS 714:2025 certification:
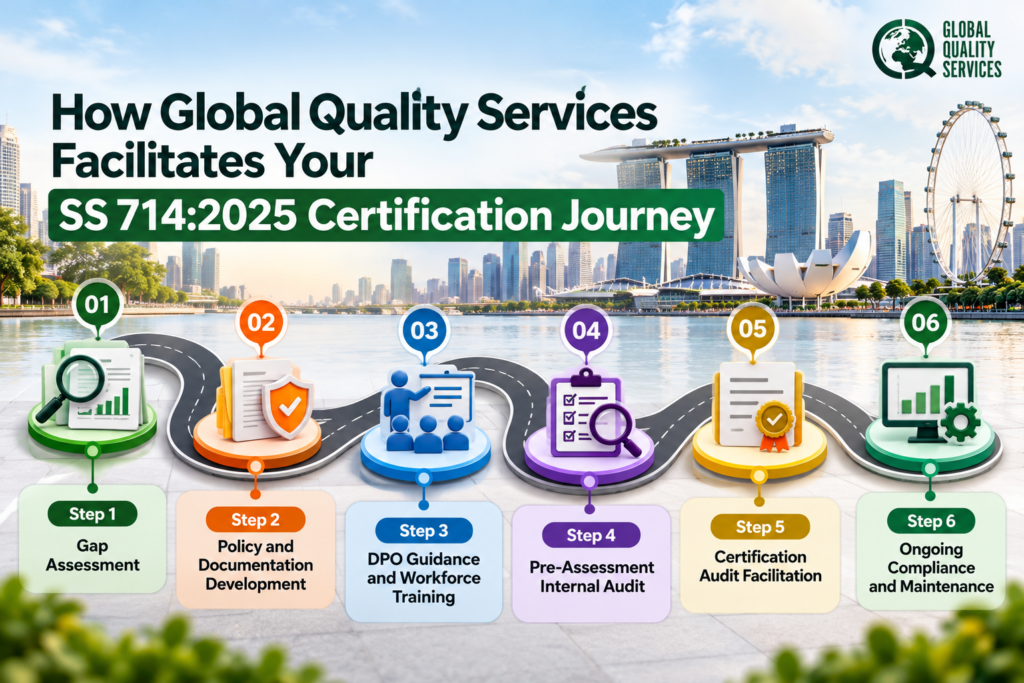
Step 1: Gap Assessment
We review your current data protection policies and technical controls against SS 714:2025 standards. You receive a clear roadmap outlining every requirement needed before official evaluation.
Step 2: Policy and Documentation Development
We draft and refine all required governance documents. This includes your Data Protection Policy, DPO appointment letter, consent notices, breach response workflows, vendor agreements, and data disposal schedules.
Step 3: DPO Guidance and Workforce Training
We equip your Data Protection Officer with the exact tools required by PDPC guidelines. Our team handles official PDPC registration, DPO Connect setup, and staff privacy training. This integrates smoothly with our ISO 27701 advisory support.
Step 4: Pre-Assessment Internal Audit
We run a comprehensive internal audit to locate and close remaining gaps before official assessment. This process mirrors the proven methodology from our ISO 27001 and SOC 2 advisory programs.
Step 5: Certification Audit Facilitation
We prepare your team for Stage 1 document reviews and Stage 2 audits conducted by an IMDA-accredited certification body. Our advisors support you through all auditor queries and evidence verification.
Step 6: Ongoing Compliance and Maintenance
We offer ongoing advisory support to maintain your active certification status. Our team assists with annual surveillance audit prep, regulatory policy updates, and routine staff refresher training.
SS 714:2025 Works Well With These Certifications
SS 714:2025 does not exist in isolation. GQS Singapore integrates it with your broader data protection and security programme:
- ISO 27001 Information Security Management — The most common combination. ISO 27001 covers your information security controls. DPTM covers your data governance and accountability practices. Together, they give you complete data protection coverage
- ISO 27701 Privacy Information Management — Extends ISO 27001 specifically to privacy. Running ISO 27701 and DPTM together satisfies both technical and governance data protection requirements simultaneously
- SOC 2 Certification — For technology and cloud service providers whose US clients require SOC 2 alongside Singapore’s DPTM
- VAPT — Vulnerability Assessment and Penetration Testing — Demonstrates that your technical controls protecting personal data have been independently tested and verified
- ISO 27001 + HIPAA — For healthcare organisations managing both Singapore PDPA and US HIPAA obligations alongside DPTM
Prepare Your Business for SS 714:2025 Today
Building strong data governance protects your revenue, strengthens client trust, and gives your business a distinct competitive edge. Contact our advisory team today to schedule an initial consultation and start your SS 714:2025 compliance roadmap.
Frequently Asked Questions
1. Is SS 714:2025 mandatory in Singapore?
DPTM is voluntary but it is increasingly expected by government agencies, enterprise clients, and tender requirements. Organisations handling sensitive personal data should treat it as a practical necessity for competitive positioning.
2. How is SS 714:2025 different from the old DPTM?
SS 714:2025 is the upgraded version formalised as a Singapore Standard in July 2025. It introduces clearer requirements, annual surveillance audits for ongoing compliance assurance, and accredited certification bodies overseen by SAC.
3. How long does SS 714:2025 certification take with GQS Singapore?
Most organisations complete the process in 2 to 4 months, depending on how much of the required data protection framework is already in place. GQS Singapore gives you a realistic timeline after the initial gap assessment.
4. Can SS 714:2025 be combined with ISO 27001 certification?
Yes, and this is our most requested combination. ISO 27001 and SS 714:2025 share significant common ground in data protection controls and governance. Running both together saves time and cost significantly.
5. Do we need a full-time DPO to get certified?
No. Your organisation must appoint a DPO, but this can be an internal staff member with proper training or an outsourced DPO arrangement. GQS Singapore advises on the most practical option for your organisation’s size and structure.