Jurong East is an important business and connectivity hub in western Singapore, surrounded by technology companies, business parks, research organizations and advanced manufacturing activities. The wider Jurong ecosystem is increasingly connected to digital transformation, automation, AI and technology-enabled operations.
For organizations serving enterprise customers from Jurong East, SOC 2 Type 2 can provide independent assurance that relevant controls are appropriately designed and operating effectively over a defined examination period.
What Is SOC 2 Type 2?
SOC 2 Type 2 Certification in Jurong East is an independent attestation examination based on the AICPA Trust Services Criteria. Depending on the engagement scope, the criteria cover Security, Availability, Processing Integrity, Confidentiality, and Privacy.
Unlike Type 1, which evaluates controls at a specific point in time, Type 2 evaluates whether relevant controls operated effectively throughout a defined period.
SOC 2 Type 2 is therefore not an ISO-style certification. An independent service auditor or CPA firm performs the examination and issues the SOC 2 report.
Latest SOC 2 Type 2 Development: AICPA Issues New AI Examination Guidance
A significant 2026 development is the AICPA’s TQA Section 9561, issued on 11 September 2026. The guidance explains how a service organization’s use of artificial intelligence can affect SOC 1 and SOC 2 examinations under the applicable AICPA attestation standards.
This is particularly relevant for technology and AI-driven oorganizationsin the Jurong East area. Businesses using AI in customer-facing services, internal systems, or third-party platforms may need to consider how AI affects areas such as data handling, access controls, monitoring, risk management, and system processes.
The update does not create a new “SOC 2 2026” framework. AICPA’s current resource library still references the 2017 Trust Services Criteria with Revised Points of Focus from 2022.
Why SOC 2 Matters for Businesses in Jurong East
Jurong East sits within a wider western Singapore ecosystem that connects commercial activity with technology, research and industrial development. The nearby Jurong Innovation District includes advanced manufacturing, precision engineering, autonomous mobility and clean technology companies.
The area also connects to International Business Park and other technology-oriented business locations. This creates a strong environment for companies handling business data, cloud services, connected technologies, software and digitally enabled operations.
For these organizations, SOC 2 Type 2 can provide useful independent evidence during enterprise procurement, customer security reviews, vendor assessments, and third-party due diligence.
Who Should Consider SOC 2 Type 2 Certification in Jurong East?
These are the major industries that must consider SOC 2 Type 2 Certification in Jurong East:
Technology and SaaS Companies
Software providers serving enterprise customers can use SOC 2 Type 2 to demonstrate that relevant security and operational controls have been consistently maintained.
AI and Data Companies
Companies developing or operating AI and data-driven services can use SOC 2 as part of a broader control environment covering access, data protection, monitoring and risk management.
Advanced Manufacturing Technology Providers
Jurong’s wider innovation ecosystem includes advanced manufacturing and Industry 4.0 activities. Technology providers supporting connected manufacturing, automation, industrial software or digital platforms may benefit from demonstrating stronger control practices.
Cloud and IT Service Providers
Cloud, managed service and technology providers handling customer systems or sensitive information may encounter SOC 2 requirements during enterprise procurement and vendor assessments.
Businesses Serving Financial or Enterprise Customers
Organizations supplying technology or digital services to banks, financial institutions, multinational companies and other security-conscious customers may use SOC 2 Type 2 to strengthen third-party assurance.
Benefits of SOC 2 Type 2 in Jurong East
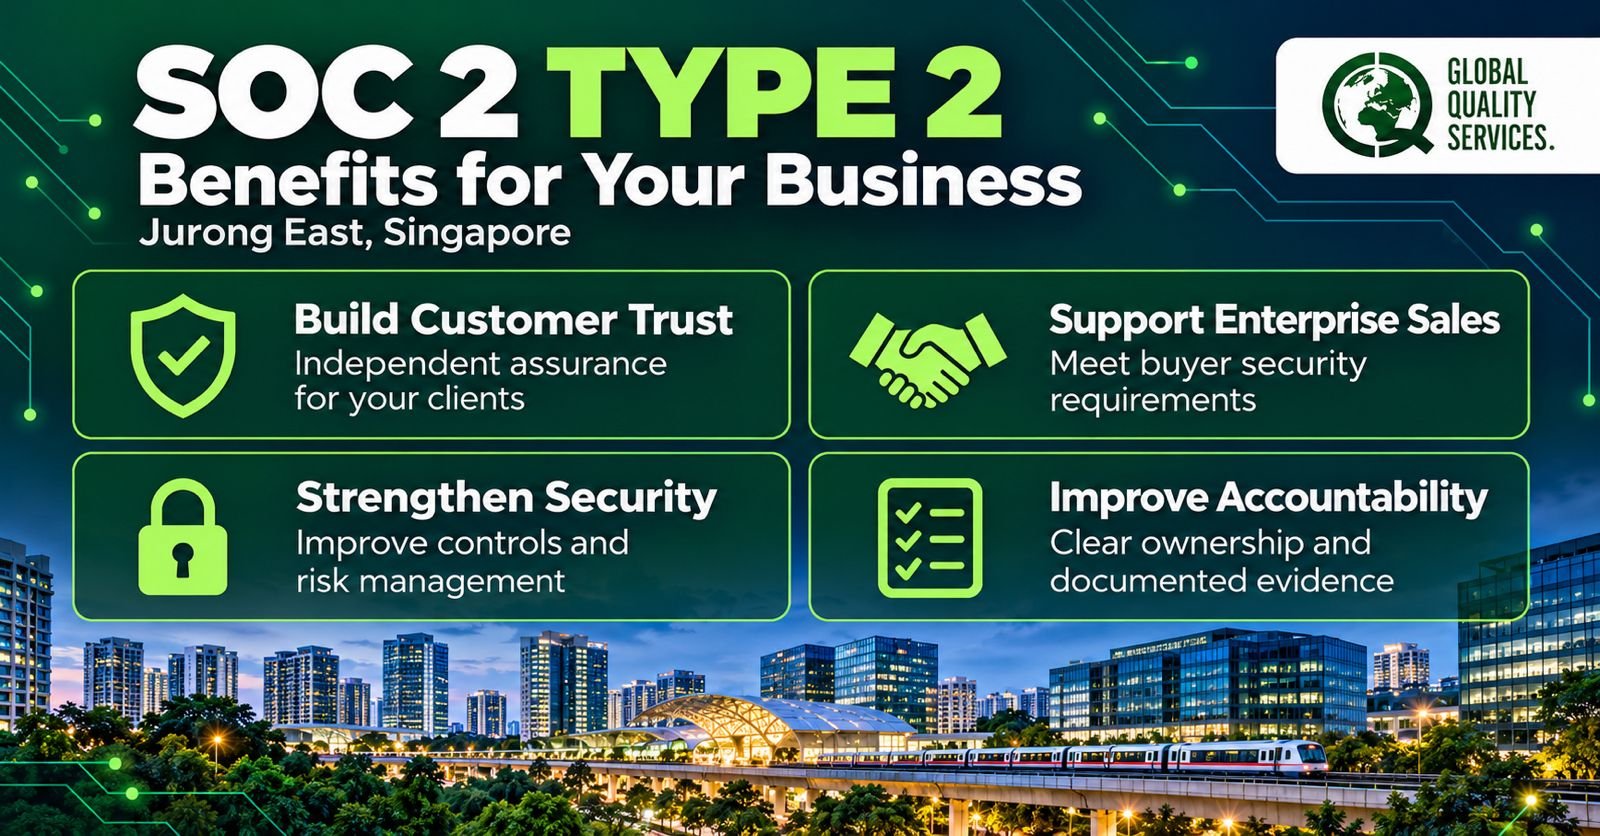
Strengthen Customer Confidence
A SOC 2 Type 2 report provides independent assurance that relevant controls operated effectively over a defined period.
Support Enterprise Sales
Large customers often require evidence of security and control practices before approving technology vendors. SOC 2 can provide structured evidence during these reviews.
Improve Third-Party Risk Management
SOC 2 documentation can support vendor questionnaires, procurement reviews and customer due diligence by providing information about the organization’s control environment.
Strengthen Technology Governance
Preparing for a Type 2 examination encourages organizations to maintain consistent processes for access management, monitoring, incident management, change management and evidence collection.
Support International Business
A SOC 2 Type 2 report can help Singapore-based technology companies communicate their control environment to customers and partners in international markets.
What Does SOC 2 Type 2 Cover?
The scope depends on the organization’s services and selected Trust Services Criteria.
Security
Controls may address access management, authentication, security monitoring, vulnerability management, incident response and change management.
Availability
Where selected, controls can cover system availability, monitoring, capacity management, backup and disaster recovery.
Processing Integrity
This addresses whether system processing is complete, accurate, timely, valid and authorized.
Confidentiality
Controls focus on protecting information designated as confidential against unauthorized access, disclosure or use.
Privacy
Where included in the engagement, Privacy criteria address areas such as personal information collection, use, retention, disclosure and disposal.
SOC 2 Type 2 and Singapore Regulatory Requirements
SOC 2 does not replace Singapore’s legal or regulatory requirements.
The Personal Data Protection Act (PDPA) establishes obligations for organizations handling personal data. SOC 2 can support relevant privacy and security controls, but it does not automatically demonstrate complete PDPA compliance.
Organizations operating in or serving Singapore’s financial sector may also need to address applicable MAS requirements relating to technology risk, cybersecurity, outsourcing and operational resilience. SOC 2 can support assurance and vendor due diligence but does not replace applicable MAS requirements.
SOC 2 Type 2 Readiness Checklist
Before beginning the independent examination, organizations should define the system and services within scope and determine which Trust Services Criteria apply.
They should then review access controls, security monitoring, incident management, risk management, change management, and third-party controls.Collect evidenced consistently throughout the examination period. A readiness assessment can identify gaps before the independent service auditor begins testing.
SOC 2 Type 2 Examination Process in Jurong East
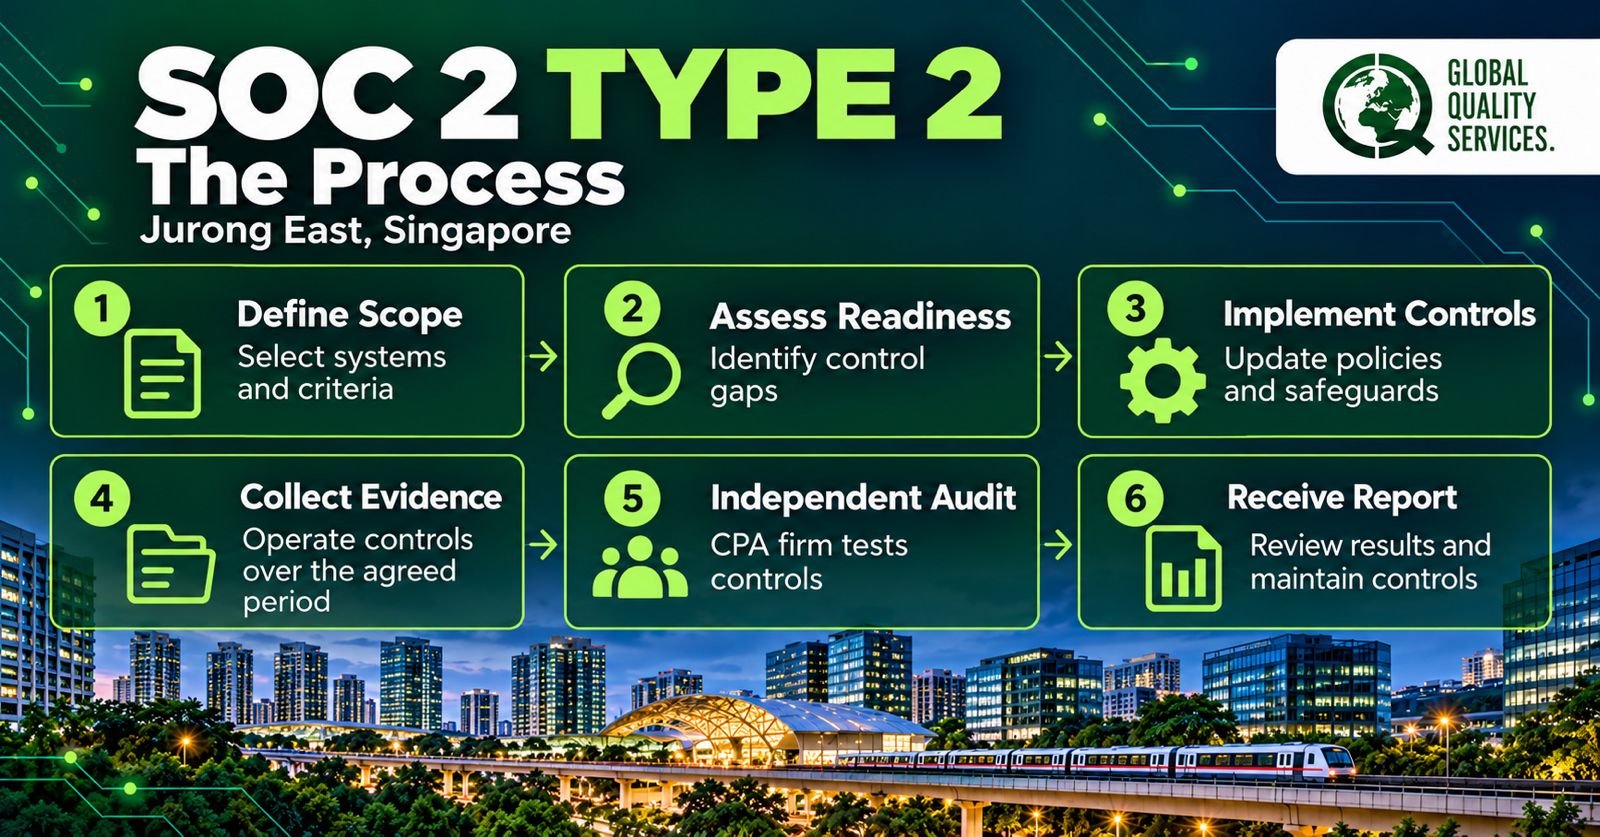
1. Define the Scope
Identify the services, systems, applications, infrastructure and processes included in the SOC 2 examination.
2. Select the Trust Services Criteria
Determine which criteria apply based on the organization’s services, commitments and risk environment.
3. Conduct a Readiness Assessment
Review existing policies, controls, and evidence to identify gaps to address before the examination.
4. Strengthen the Control Environment
Implement or improve relevant controls covering security, access, monitoring, risk management and operational processes.
5. Operate and Collect Evidence
Controls must operate consistently during the defined examination period, with appropriate evidence retained.
6. Complete the Independent Examination
The independent service auditor evaluates the relevant controls and tests their operating effectiveness.
7. Receive the SOC 2 Type 2 Report
After completing the examination, the independent service auditor issues the SOC 2 Type 2 report.
How Can GQS Help With SOC 2 Type 2 in Jurong East?
Global Quality Services can support organizations with SOC 2 Type 2 readiness through scope assessment, gap assessment, control documentation, implementation support, evidence preparation and examination readiness. GQS can also help organizations understand how their SOC 2 control environment can work alongside Singapore requirements such as the PDPA, MAS expectations and the Cyber Trust framework. The independent service auditor remains responsible for the formal SOC 2 examination and report.
Frequently Asked Questions
Is SOC 2 Type 2 mandatory in Singapore?
No. SOC 2 Type 2 is not a general legal requirement in Singapore. However, enterprise customers, technology partners, or business clients may require a SOC 2 report as part of their vendor or security assessment.
Is SOC 2 Type 2 a certification?
No. SOC 2 Type 2 is an independent attestation repor, notn an ISO-style certification.
Is SOC 2 Type II recognized as equivalent to ISO/IEC 27001 for Cyber Trust?
No. CSA currently recognizes ISO/IEC 27001 as the recognized equivalent for Cyber Trust Mark. SOC 2 Type II is not currently recognized as an equivalent.
Does SOC 2 Type 2 demonstrate PDPA compliance?
No. SOC 2 may support relevant privacy and security controls, but it does not automatically demonstrate full PDPA compliance.
Does the 2026 AICPA AI guidance create a new SOC 2 standard?
No. AICPA’s September 2026 TQA Section 9561 provides guidance on how a service organization’s use of AI can affect SOC 1 and SOC 2 examinations. It does not replace the existing Trust Services Criteria.
Who issues the SOC 2 Type 2 report?
An independent service auditor or qualified CPA firm performs the examination and issues the SOC 2 Type 2 report.