Global Quality Services provides end-to-end SOC 2 consultancy for technology companies, SaaS providers, fintech operators, and managed service providers based in Bangsar South. We cover readiness assessments, Trust Services Criteria gap analysis, controls implementation, internal audit preparation, and full SOC 2 audit readiness. Our engagements are aligned with Malaysia’s evolving data protection and cybersecurity regulatory environment.
Bangsar South is Kuala Lumpur’s premier technology and financial services district. Developed by UOA Group, it spans 60 acres and is a designated MSC Malaysia Cybercentre. It hosts global companies including Adyen, Wise, SC Johnson Asia-Pacific, and Jirnexu alongside hundreds of technology startups, financial services firms, and regional headquarters. In 2024, the Malaysian government designated the KL Sentral and Bangsar South corridor as the KL20 Startup Hub, positioning it as a national priority zone for global technology companies. For Bangsar South operators handling customer data and running cloud-based services, SOC 2 certification is increasingly a commercial requirement from US, European, and enterprise clients.
What Is SOC 2
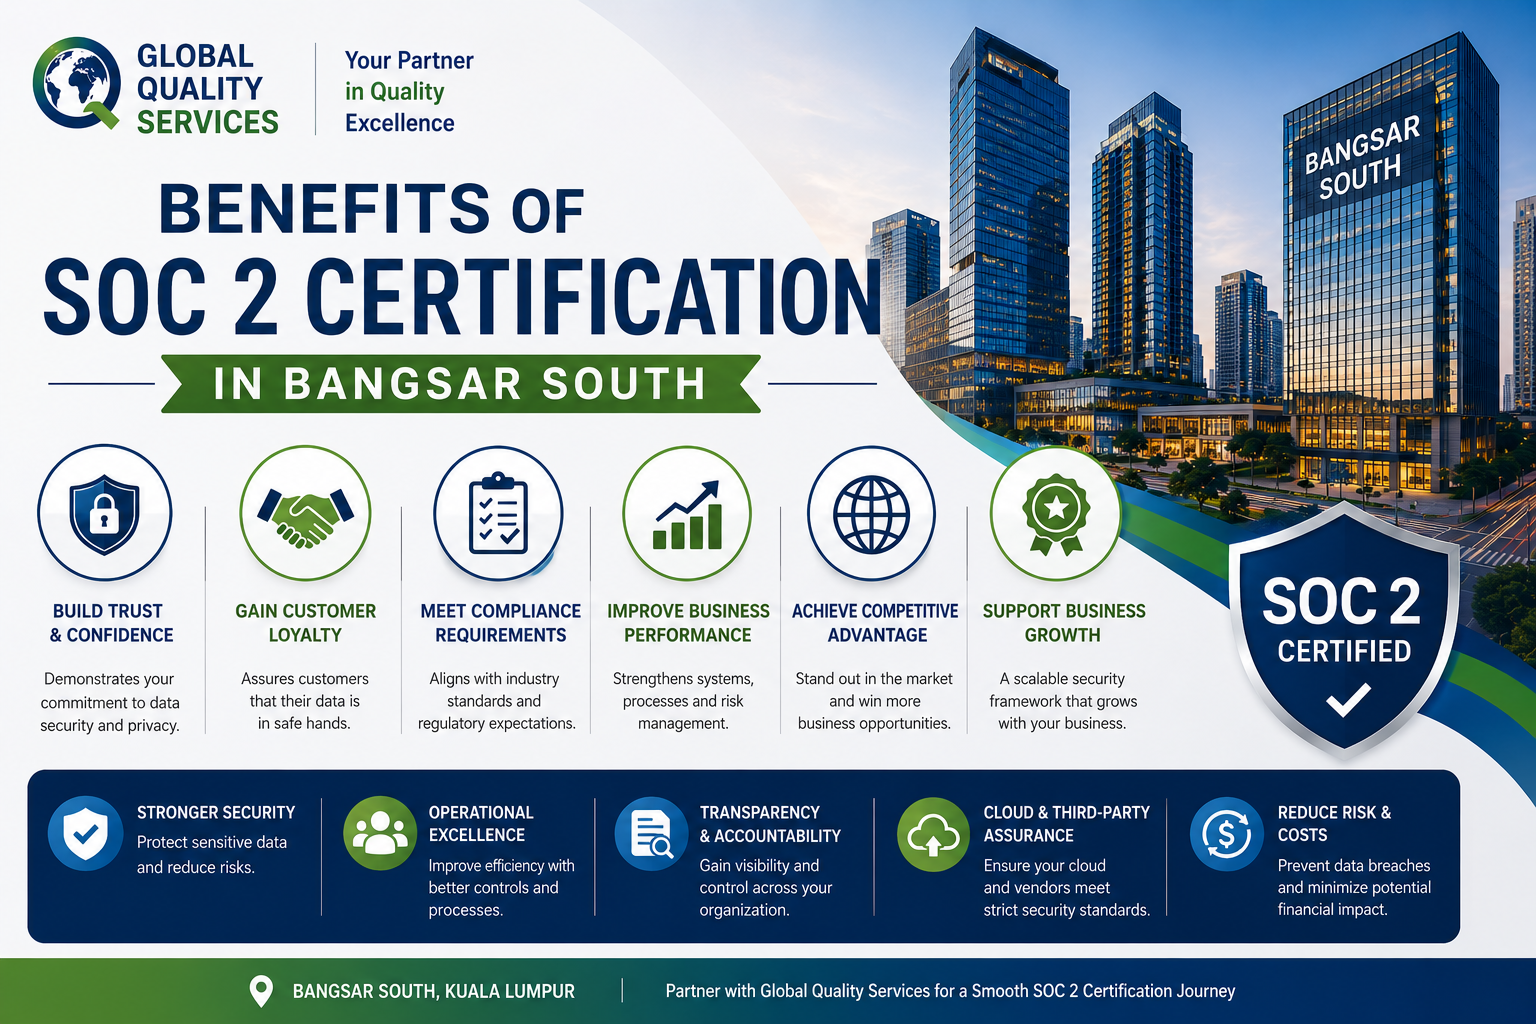
SOC 2 is a data security and privacy assurance framework developed by the American Institute of Certified Public Accountants (AICPA). It is designed for service organizations that store, process, or transmit customer data. It evaluates controls against the AICPA Trust Services Criteria (TSC).
SOC 2 has five Trust Services Criteria:
- Security (Common Criteria): Mandatory for all SOC 2 reports. Covers access controls, threat detection, incident response, and system monitoring.
- Availability: Covers system uptime commitments, performance monitoring, and business continuity controls.
- Processing Integrity: Covers complete, accurate, timely, and authorized data processing.
- Confidentiality: Covers protection of information designated as confidential, including encryption and access restrictions.
- Privacy: Covers collection, use, retention, disclosure, and disposal of personal information aligned to privacy notice commitments.
SOC 2 has two report types:
- SOC 2 Type I: A point-in-time assessment. It confirms that controls are suitably designed to meet the selected Trust Services Criteria.
- SOC 2 Type II: A period-in-time assessment, typically covering six to twelve months. It confirms that controls operated effectively throughout the audit period. Enterprise and US-market buyers almost always require Type II.
Why SOC 2 Matters for Bangsar South Companies
Bangsar South’s technology ecosystem is outward-facing. The companies here sell SaaS platforms, payment infrastructure, data analytics, managed services, and financial technology to US, European, and enterprise buyers across Asia. Those buyers have a standard question in every vendor qualification process: do you have SOC 2?
Three things are driving SOC 2 demand in Bangsar South right now.
Enterprise and US buyers require it.
Large organizations now demand that suppliers demonstrate cybersecurity maturity via SOC 2 Type II certification, ISO 27001, and regular penetration testing results. For Bangsar South SaaS companies and fintech operators selling into US markets or to enterprise procurement teams, SOC 2 Type II is a vendor qualification gate. Without it, deals stall or fail.
Malaysia’s regulatory environment is tightening.
Malaysia’s Personal Data Protection Act (PDPA), with its 2024 amendments, introduces mandatory breach notification and increased penalties of up to RM 500,000 per offence. The Cyber Security Act 2024 (CSA 2024) introduced mandatory requirements for Critical National Information Infrastructure (CNII) operators and prescribed cybersecurity service providers. BNM’s Risk Management in Technology (RMiT) framework mandates specific security controls and annual penetration testing for financial institutions, directly affecting fintech operators in Bangsar South. SOC 2 controls address all of these frameworks simultaneously.
The KL20 Startup Hub designation raises the bar.
Bangsar South is now a national-priority technology zone. The KL20 Summit is targeting Malaysia to be in the top 20 global startup hubs by 2030, attracting global startups, founders, and VC firms to relocate to Kuala Lumpur. Global investors and strategic partners applying global due diligence standards will expect SOC 2 certification from Bangsar South companies in their portfolio or pipeline.
Who in Bangsar South Needs SOC 2
SOC 2 applies to any service organization that handles customer data as part of its service delivery. In Bangsar South, that covers:
- SaaS and cloud platform providers serving enterprise or US-market customers
- Fintech and payment technology companies handling financial transaction data
- Managed service providers and IT outsourcing firms managing customer systems and data
- Data analytics and business intelligence platforms processing customer or user data
- HR technology, procurement technology, and enterprise software providers
- Regional headquarters of multinational companies that must demonstrate data security to parent company or audit requirements
- Startups raising Series A or beyond from US or global VC firms who require SOC 2 as a diligence condition
SOC 2 vs ISO 27001: Which Does a Bangsar South Company Need
Both standards address information security. They serve different primary audiences.
- SOC 2 is a US market standard developed by the AICPA. It produces an auditor’s report used by buyers to assess a vendor’s data security controls. It is the default requirement in US enterprise procurement and VC diligence. It does not result in a certificate. It results in an audit report.
- ISO 27001 is an international management system standard. It results in a globally recognized certificate. It is the preferred standard in European, Asian, and government procurement contexts.
Many Bangsar South companies need both. US-facing SaaS and fintech companies typically lead with SOC 2. Companies with European or Malaysian government clients lead with ISO 27001. GQS can scope and deliver both within a single integrated engagement, avoiding duplication of controls documentation and audit preparation effort.
Key SOC 2 Requirements
These requirements apply regardless of which Trust Services Criteria are selected:
- Access Control: Logical access to systems and data must be restricted to authorized users. Includes user provisioning, role-based access, multi-factor authentication, and access reviews.
- Risk Assessment: Identify threats, vulnerabilities, and potential impacts to systems and data. Must be documented and repeated on a defined cycle.
- Incident Response: Maintain documented procedures for detecting, containing, investigating, and recovering from security incidents. Evidence of actual incident management is required for Type II.
- Change Management: Control changes to production systems through a documented and approved change management process.
- Vendor Management: Assess and monitor third-party vendors and subprocessors that have access to customer data or systems within scope.
- Availability Monitoring: For organizations selecting the Availability criterion, maintain uptime monitoring, alerting, and documented SLA performance evidence.
- Encryption: Protect data in transit and at rest using industry-standard encryption. Document encryption standards and key management practices.
- Logging and Monitoring: Maintain system activity logs. Implement alerting for anomalous activity. Retain logs for the period required by your audit scope.
- Business Continuity and Disaster Recovery: Maintain documented, tested BC/DR plans that cover recovery time and recovery point objectives for systems within scope.
- Security Awareness Training: All personnel must complete documented security awareness training on a defined cycle.
Steps to Get SOC 2 Certified in Bangsar South
Here are the steps that help businesses to get SOC 2 certified:
Step 1: Define Scope and Trust Services Criteria
Identify which systems, services, and data flows are in scope. Select the Trust Services Criteria relevant to your customers and commercial requirements. Security is mandatory. Additional criteria depend on what your buyers and contracts require.
Step 2: Readiness Assessment
Compare your current controls against the selected Trust Services Criteria. Identify gaps. Produce a prioritized remediation plan. This is the foundation of the entire engagement.
Step 3: Controls Implementation
Build and document the controls needed to meet your selected criteria. This includes policies, procedures, technical configurations, access management systems, monitoring tools, and vendor management processes.
Step 4: Evidence Collection
For SOC 2 Type II, controls must operate effectively over the audit period. Start collecting evidence from day one of the observation window. Evidence includes access review records, change management logs, incident tickets, training completion records, and vendor assessment documentation.
Step 5: Internal Audit
Conduct an internal review of all controls against the selected Trust Services Criteria. Identify gaps in evidence or control operation. Close them before engaging the external auditor.
Step 6: Auditor Engagement
Engage a licensed CPA firm authorized to issue SOC 2 reports. For Type I, the auditor assesses design suitability at a point in time. For Type II, the auditor assesses operating effectiveness over the full audit period.
Step 7: Report Issuance and Remediation
The auditor issues the SOC 2 report. Any exceptions or qualifications in the report must be addressed before the report is shared with customers or used in procurement. GQS supports post-report remediation and prepares you for the next audit cycle.
Malaysia Regulatory Context for Bangsar South Operators
Bangsar South technology companies operate within a layered Malaysian regulatory framework:
- Personal Data Protection Act 2010 (PDPA): Malaysia’s primary data protection legislation, enforced by the Department of Personal Data Protection (JPDP). The 2024 amendments introduced mandatory breach notification requirements and increased penalties. SOC 2 controls for incident detection, logging, and response directly support PDPA compliance.
- Cyber Security Act 2024: Administered by the National Cyber Security Agency (NACSA). Introduces mandatory obligations for CNII operators across 11 critical sectors and licensing requirements for prescribed cybersecurity service providers. SOC 2 security controls align with CSA 2024 governance and risk management requirements.
- BNM Risk Management in Technology (RMiT): Applies to financial institutions and is increasingly relevant to fintech operators in Bangsar South. Mandates specific technology risk governance, access management, incident response, and third-party risk management controls. SOC 2 Type II evidence packages support RMiT audit requirements.
- Communications and Multimedia Act 1998 (CMA): Enforced by the Malaysian Communications and Multimedia Commission (MCMC). Applies to Bangsar South companies holding telecommunications or content service licenses. SOC 2 monitoring and incident response controls support CMA cybersecurity obligations.
- MSC Malaysia Status Requirements: Bangsar South is an MSC Malaysia Cybercentre. MSC-status companies are subject to Malaysia Digital Economy Corporation (MDEC) guidelines including commitments to internationally recognized data protection and security standards.
Industries in Bangsar South That Benefit from SOC 2
Fintech and Payment Technology
Adyen opened its Bangsar South office in 2022. Wise also operates in the Bangsar South area. Soft Space, a payment technology provider at Tower 6, Avenue 5, develops banking-grade payment infrastructure sold to financial institutions across Asia. Jirnexu, at Vertical Corporate Tower B, runs financial comparison and data platforms serving enterprise clients. These companies operate in a sector where SOC 2 Type II is a baseline expectation from bank partners, enterprise clients, and global payment scheme auditors.
SaaS and Cloud Platform Providers
Bangsar South hosts a significant cluster of SaaS companies serving regional and global enterprise customers. US-market enterprise procurement requires SOC 2 Type II from all cloud and SaaS vendors. For Bangsar South SaaS operators expanding into the US or handling US customer data, SOC 2 is the first compliance question in every enterprise sales cycle.
Managed Service and IT Outsourcing Providers
MSPs and IT outsourcing operators in Bangsar South manage customer systems, networks, and data. Their enterprise clients increasingly require evidence of data security controls through a SOC 2 report rather than a questionnaire alone. SOC 2 Type II provides that evidence in a format auditors and procurement teams can assess directly.
Regional Headquarters of Multinational Companies
SC Johnson’s Asia-Pacific Regional Headquarters is located in Bangsar South. Regional headquarters of multinational companies routinely receive SOC 2 requirements from parent company internal audit, global procurement teams, or group-level cybersecurity governance programs.
Startups Raising Institutional Capital
The KL20 initiative is targeting global startups and VC firms to relocate to Kuala Lumpur. US and global VC firms conducting diligence on Bangsar South portfolio companies routinely require SOC 2 Type II as a condition of investment or as a milestone in the post-investment roadmap. Starting SOC 2 early reduces the time and cost of meeting that condition under deal-pressure timelines.
Data Analytics and Business Intelligence Platforms
Analytics and BI platforms process large volumes of customer and user data. Enterprise buyers evaluate the security of that processing through SOC 2 reports. For Bangsar South analytics companies selling to enterprise clients in regulated industries, SOC 2 is a direct commercial enabler.
Why Global Quality Services
GQS has delivered SOC 2 readiness and certification support engagements across Southeast Asia’s technology sector. We understand how Bangsar South technology companies sell, what their buyers require, and how Malaysia’s regulatory environment intersects with US-standard compliance frameworks.
We do not deliver generic compliance templates. Every SOC 2 engagement starts from your actual system architecture, your customer contracts, and the Trust Services Criteria your buyers specifically require.
With GQS, Bangsar South companies receive:
- Readiness assessment mapped to your selected Trust Services Criteria and your specific system and data scope
- Controls gap analysis with a prioritized remediation plan tied to your audit timeline
- Full policies and procedures documentation aligned to AICPA Trust Services Criteria
- Technical controls implementation support covering access management, logging, monitoring, encryption, and vendor management
- Evidence collection framework and templates for the SOC 2 Type II observation period
- Internal audit facilitation against selected Trust Services Criteria before external auditor engagement
- Auditor selection support and pre-audit coordination
- Post-report remediation support and preparation for the next audit cycle
- Scope extension to ISO 27001 for Bangsar South companies requiring both US-market SOC 2 and international ISO certification
- Integration with ISO 27701 for organizations with PDPA and privacy compliance requirements alongside SOC 2
- Combined scoping with VAPT services for Bangsar South companies requiring penetration testing evidence as part of their SOC 2 or BNM RMiT compliance package
Contact Global Quality Services to start your SOC 2 certification engagement in Bangsar South.
Frequently Asked Questions
What is SOC 2 and does my Bangsar South company need it?
SOC 2 is a data security assurance framework developed by the AICPA for service organizations handling customer data. If your Bangsar South company provides SaaS, cloud services, managed IT, payment technology, or data processing to US enterprise buyers, you almost certainly need it. Enterprise procurement teams and US-market clients require SOC 2 Type II as a vendor qualification standard. It is also increasingly required by VC firms conducting investment diligence on Malaysian technology companies.
What is the difference between SOC 2 Type I and Type II?
SOC 2 Type I is a point-in-time assessment confirming that controls are suitably designed. SOC 2 Type II covers a period of typically six to twelve months and confirms that controls operated effectively throughout that period. Enterprise and US-market buyers almost always require Type II. Type I is useful as an interim step while building toward Type II, or for early-stage companies needing to demonstrate initial control design before the observation period is complete.
How long does SOC 2 Type II take for a Bangsar South company?
Most Bangsar South technology companies complete readiness assessment through to SOC 2 Type II report issuance in nine to fourteen months. The readiness and controls implementation phase typically takes three to six months. The Type II audit observation period then runs for six to twelve months. Companies with mature existing information security controls, documented policies, and existing ISO 27001 certification can move faster. GQS provides a detailed timeline during the readiness assessment.
Does SOC 2 satisfy Malaysia’s PDPA requirements?
SOC 2 directly supports PDPA compliance but does not replace it. SOC 2 controls for incident detection, logging, response, access management, and vendor management address the technical controls that underpin PDPA’s breach notification and data protection obligations. However, PDPA also has specific data subject rights, consent, and cross-border transfer requirements that sit outside SOC 2 scope. GQS can scope a combined engagement that addresses both SOC 2 and PDPA requirements within a single controls framework.
Can GQS combine SOC 2 with ISO 27001 for a Bangsar South company?
Yes. Many Bangsar South companies need both. SOC 2 is required for US-market and enterprise buyers. ISO 27001 is required for European, Asian government, and internationally focused procurement. The controls overlap significantly. GQS designs a unified controls framework that satisfies both simultaneously, avoiding duplication of documentation, training, and audit preparation effort. Combined engagements also reduce overall cost compared to running two separate compliance programs.