Orchard Road is one of Singapore’s best-known commercial destinations, bringing together retail businesses, hotels, corporate offices, healthcare providers and lifestyle services. From customer loyalty programs and online shopping platforms to hotel reservations and appointment management systems, businesses in this district handle personal information through a wide range of customer-facing activities.
As these operations become increasingly digital, organizations need clear processes to manage customer records, employee information, booking details, and other personally identifiable information (PII). ISO/IEC 27701:2025 Certification in Orchard Road provides a structured framework for establishing, maintaining and continually improving a Privacy Information Management System (PIMS).
Published on 14 October 2025, ISO/IEC 27701:2025 is an international management system standard for organizations that process personally identifiable information. Global Quality Services provides certification services for businesses in Orchard Road, Singapore, seeking to demonstrate conformity with the standard and establish a systematic approach to privacy management.
ISO/IEC 27701:2025 Certification for Orchard Road Businesses
Privacy management is relevant to more than technology companies and financial institutions. Businesses that collect customer details, manage reservations, operate membership programs or maintain employee databases also have privacy responsibilities.
ISO/IEC 27701:2025 sets out requirements for managing these responsibilities through a formal system that addresses privacy risks, organizational accountability,ty and the handling of personal information.
Which Businesses in Orchard Road Can Benefit From Certification?
The standard applies to organizations of all sizes and industries, including those acting as personal information controllers, processors, or both.
Businesses that may consider certification include:
- Retailers and e-commerce companies: Organizations that handle customer accounts, purchase histories, membership records, and marketing preferences.
- Hotels and hospitality groups: Businesses that manage guest registrations, reservation details, contact information, and service requests.
- Healthcare and wellness providers: Organizations that process patient or client information in line with applicable legal and operational requirements.
- Restaurants and lifestyle businesses: Companies that manage booking records, customer profiles, loyalty programs, and digital ordering information.
- Property management and real estate firms: Organizations handling tenant details, prospective buyer information, visitor records, and employee data.
- Professional and corporate service providers: Businesses that maintain client files, recruitment records, payroll information, and other personal data.
The certification scope should reflect the organization’s actual activities and responsibilities; the standard does not automatically cover every location, subsidiary, or business function unless these are included within the defined scope.
Why Is ISO/IEC 27701:2025 Relevant to Orchard Road?
Orchard Road has a distinctive commercial environment where customer interactions, visitor services, and business operations often intersect. Companies may collect personal information through physical outlets, websites, mobile applications, reservation systems, and third-party service platforms.
This creates a practical need for consistent privacy management across different customer touchpoints.
Retail and Customer Loyalty Operations
Retailers may collect information through membership registrations, online purchases, promotional campaigns, and customer service inquiries. A PIMS helps organizations establish defined responsibilities and processes for managing the personal information involved in these activities.
Hotels and Guest Services
Hotels may process booking details, guest contact information, identification records and special service requests. Where these activities fall within the organization’s scope, privacy management arrangements can help establish accountability for how information is handled and shared with relevant service providers.
Healthcare and Personal Services
Healthcare providers and other personal service businesses may handle information requiring careful management. Their privacy arrangements should reflect the nature of the information processed, the applicable legal requirements and the organization’s responsibilities.
Digital Commerce and External Platforms
Businesses often rely on payment providers, customer relationship management systems, cloud platforms and outsourced marketing services. A privacy management system can help define responsibilities and evaluate risks associated with these third-party relationships.
Benefits of ISO/IEC 27701:2025 Certification in Orchard Road
For businesses managing customer-facing operations, certification can provide a formal basis for demonstrating how privacy responsibilities are addressed within the organization.
1. Consistent Customer Data Management
A documented PIMS helps establish consistent processes for handling personal information across physical outlets, websites, mobile applications, and customer service teams. This can make privacy responsibilities clearer as customer interactions move between channels.
2. Stronger Accountability for Privacy Decisions
Defined responsibilities and documented procedures help organizations establish who oversees relevant processing activities, how privacy risks are evaluated, and how issues are addressed.
3. Better Oversight of Marketing and Customer Relationship Activities
Businesses using customer databases, membership systems and promotional platforms can evaluate how personal information is processed and shared. This supports more structured oversight of privacy-related responsibilities.
4. Greater Confidence During Supplier Assessments
Enterprise customers, landlords, commercial partners and corporate clients may request evidence of formal privacy management arrangements. Certification can provide independent evidence that the PIMS has been assessed against the standard within the stated scope.
5. Support for Business Expansion
Organizations opening new outlets, introducing digital services or expanding into international markets may need to review their existing privacy processes. A management system provides a consistent framework for evaluating changes and maintaining accountability.
Certification does not guarantee that data breaches will not occur or automatically establish compliance with all applicable privacy laws. Its value depends on effectively implementing and maintaining the PIMS.
ISO/IEC 27701:2025 Certification Process With Global Quality Services
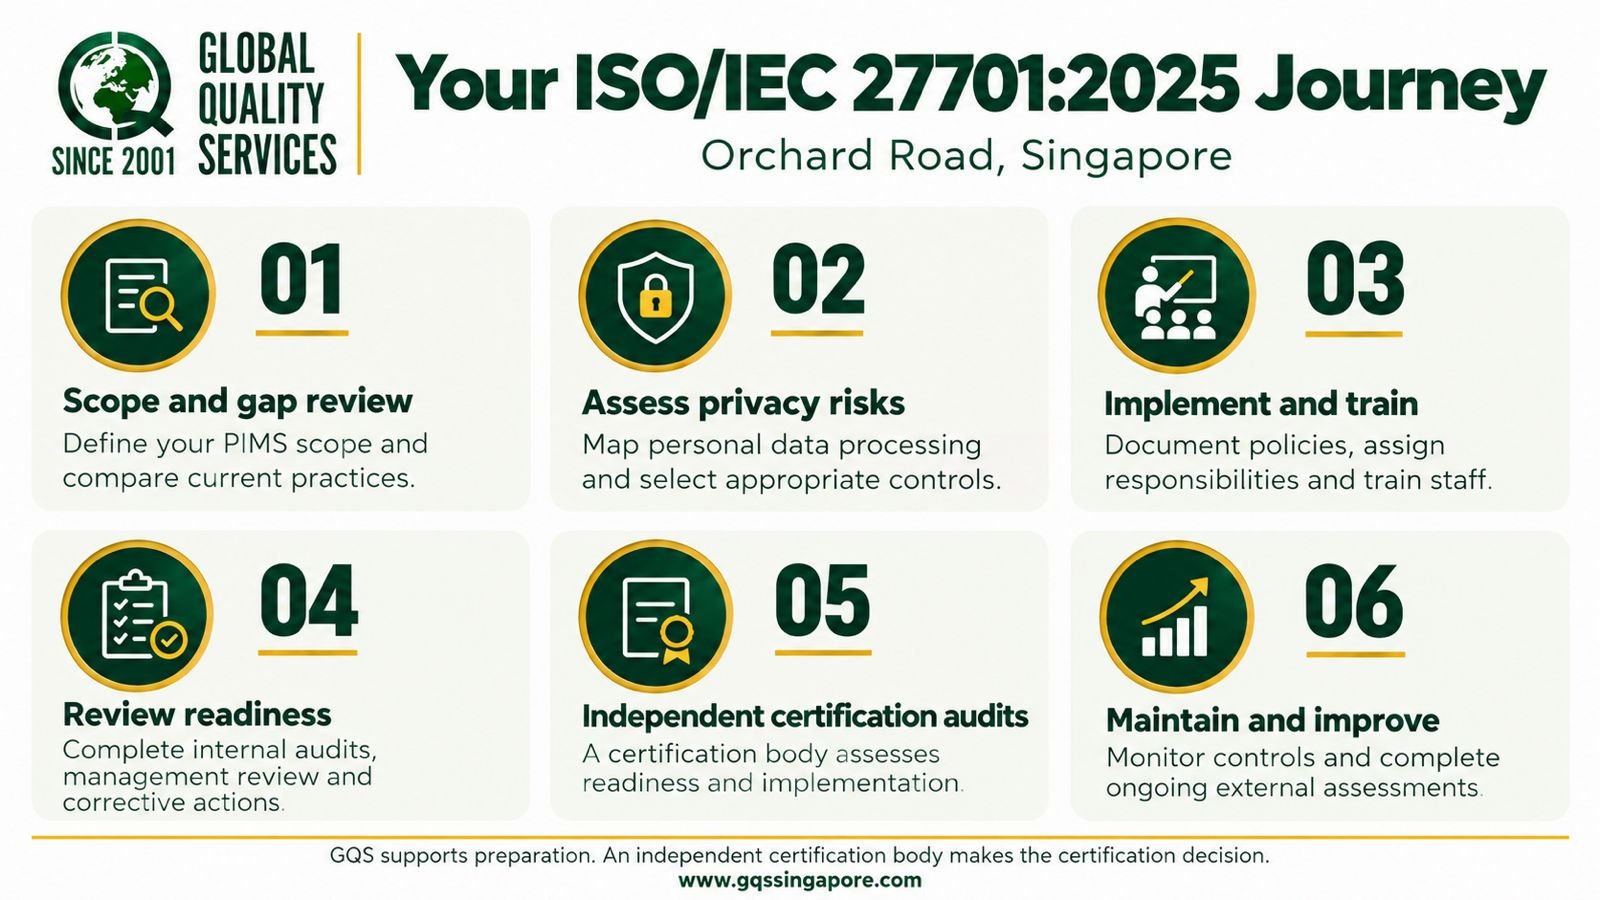
The certification process evaluates whether an organization’s Privacy Information Management System meets the applicable requirements of ISO/IEC 27701:2025.
Define the Scope of Certification
The organization identifies the services, departments, locations, and personal information processing activities to be covered. For example, a retail group may need to define whether the scope includes its head office, selected outlets, e-commerce operations, or other relevant functions.
Evaluate the Existing Management System
The organization’s privacy policies, risk assessments, responsibilities, documented processes, and supporting records are reviewed against the applicable standard requirements.
Conduct the Certification Audit
The audit evaluates the PIMS within the agreed scope using relevant documentation and objective evidence. The assessment considers whether the management system meets the applicable requirements.
Address Audit Findings
If nonconformities are identified, the organization must implement appropriate corrective actions and provide the necessary evidence for review under the certification process.
Complete the Certification Decision
Certification is granted only after the applicable requirements have been met and the certification decision has been completed. Ongoing surveillance or other follow-up activities depend on the relevant certification arrangements.
ISO/IEC 27701:2025 and Singapore’s PDPA
Businesses in Orchard Road should consider their privacy management arrangements alongside Singapore’s Personal Data Protection Act 2012 (PDPA).
The PDPA sets out obligations for organizations handling personal data within its scope, subject to applicable provisions and exceptions. Relevant responsibilities may include consent, purpose limitation, protection, retention, access and correction, and transfers of personal data outside Singapore.
For example, a hotel may need to consider how it collects and shares guest information. In contrast, a retailer may need to evaluate how it handles membership records and customer contact details. The specific obligations depend on the organization’s activities and circumstances.
ISO/IEC 27701:2025 provides a management system framework for organizing privacy responsibilities and addressing relevant risks. Certification does not automatically establish full compliance with Singapore’s PDPA, nor does it replace a legal assessment of the organization’s obligations.
Businesses processing personal information across borders should also evaluate the privacy laws applicable in the relevant jurisdictions.
ISO/IEC 27701:2025 vs ISO/IEC 27001: Choosing the Right Standard
Organizations planning a certification program should understand the distinction between privacy management and information security management.
| Comparison | ISO/IEC 27701:2025 | ISO/IEC 27001 |
|---|---|---|
| Primary purpose | Establish a Privacy Information Management System | Establish an Information Security Management System |
| Main focus | Privacy responsibilities associated with personal information | Information security risks and controls |
| Business relevance | Personal information processing and privacy governance | Protecting information assets across the organization |
| Standalone status | A standalone management system standard in the 2025 edition | A separate information security management standard |
| Relationship | Can complement an information security management system | Does not automatically establish conformity with ISO/IEC 27701:2025 |
The appropriate standard depends on the organization’s objectives and risk profile. Businesses may pursue both standards where they need to address privacy and wider information security requirements.
Transitioning From ISO/IEC 27701:2019 to the 2025 Edition
Organizations with an existing ISO/IEC 27701:2019 certificate should review their certification arrangements after the 2025 edition is published.
The newer edition establishes ISO/IEC 27701 as a standalone management system standard rather than an extension dependent on ISO/IEC 27001. This change means existing certificate holders must evaluate the revised requirements and their implications for the current PIMS.
Before arranging an assessment, organizations should:
- Review the 2025 edition against their existing privacy management arrangements.
- Identify changes required in policies, responsibilities, documented processes and other relevant controls.
- Reassess the scope to ensure it reflects current business activities and personal information processing responsibilities.
- Confirm applicable transition, audit and certification requirements with the relevant certification provider.
An existing ISO/IEC 27001 certificate does not automatically establish conformity with ISO/IEC 27701:2025. Organizations should confirm the applicable certification arrangements rather than assume a universal transition deadline.
Obtain ISO/IEC 27701:2025 Certification in Orchard Road With Global Quality Services.
Businesses in Orchard Road operate across retail, hospitality, healthcare, professional services and other customer-focused sectors. Each may have different privacy risks depending on the information it processes, the systems it uses and the third parties involved in its operations.
Global Quality Services provides certification services for organizations seeking to demonstrate conformity with applicable management system requirements. The certification scope is determined by the organization’s activities, its privacy management responsibilities and the relevant certification requirements.
Whether your organization manages customer databases, guest records, employee information, or personal data through digital services, a defined PIMS provides a structured approach to privacy management.
Contact Global Quality Services to discuss ISO/IEC 27701:2025 Certification in Orchard Road, Singapore, and determine the appropriate certification scope for your organization.
Frequently Asked Questions
1. Does ISO/IEC 27701:2025 certification cover customer loyalty programs and marketing databases?
It can cover the privacy management activities associated with these systems when they fall within the certified scope. Retailers should consider how customer profiles are created, how marketing preferences are managed, who can access the information, and how third-party platforms process customer data.
2. Can a hotel on Orchard Road include its reservation system and guest services in the certification scope?
Yes, provided the relevant activities are included in the defined scope and meet the applicable requirements. The organization should consider reservation management, guest information, customer service operations, and relevant external service providers when determining the boundaries of its Privacy Information Management System.
3. Will an ISO/IEC 27701:2025 certificate be accepted by international retail brands and corporate partners?
Acceptance depends on the partner’s procurement policies, contractual requirements, and expectations for privacy assurance. Before pursuing certification for a specific business opportunity, ask the prospective partner whether it requires ISO/IEC 27701:2025 certification, a particular accreditation arrangement, or additional evidence of privacy controls.
4. What should a retail group consider when certifying its headquarters but operating multiple stores?
The group should determine whether the proposed scope covers only its headquarters or also includes selected stores, e-commerce operations, and other business functions. It should consider where customer information is collected, which teams manage it, and how privacy responsibilities are applied across the locations included in the scope.
5. Can ISO/IEC 27701:2025 certification help an Orchard Road business prepare for a major customer data platform upgrade?
Yes. A planned platform upgrade provides an opportunity to review privacy responsibilities, data flows, access arrangements, retention practices, and third-party processing relationships. These considerations can inform the organization’s PIMS, although certification itself is an assessment of the management system rather than approval of a particular software platform.