Singapore’s digital economy reached S$128.1 billion in 2024, contributing 18.6% of the country’s GDP, according to the Infocomm Media Development Authority (IMDA). As digital services expand across finance, technology, professional services and other industries, organizations must pay closer attention to how personal information is collected, processed and governed.
For businesses in Marina Bay, where financial institutions, multinational corporations and technology-driven enterprises operate alongside regional headquarters, privacy management is an important part of business governance. ISO/IEC 27701:2025 Certification provides an internationally recognized framework for establishing and continually improving a Privacy Information Management System (PIMS).
Global Quality Services offers ISO/IEC 27701:2025 certification services in Marina Bay, Singapore, for organizations seeking to demonstrate conformity with the standard and establish a structured approach to managing personally identifiable information (PII).
What Does ISO/IEC 27701:2025 Certification Mean for Marina Bay Businesses?
ISO/IEC 27701:2025 specifies requirements for establishing, implementing, maintaining, and continually improving a Privacy Information Management System. Published on 14 October 2025, this second edition is a standalone management system standard applicable to organizations of different sizes and across industries.
For businesses in Marina Bay, Certification provides a framework for managing privacy responsibilities across business operations, technology platforms and third-party relationships.
The standard applies to organizations that determine how personal information is processed, those that process information on behalf of other organizations, and businesses that do both.
Organizations That Can Pursue ISO/IEC 27701:2025 Certification
The standard can be relevant to a broad range of organizations operating in and around Marina Bay, including:
- Financial institutions and wealth management firms that manage investor profiles, client records, and personal financial information.
- Fintech companies and digital payment providers processing account details, transaction-related information and customer identity records.
- Regional corporate headquarters overseeing employee information, customer databases and privacy-related responsibilities across business units.
- Technology companies and cloud service providers processing personal information for enterprise customers.
- Legal, consulting and corporate services firms handling client records, confidential documents and employee data.
- Insurance and risk management businesses managing policyholder information, claims records and other sensitive personal details.
The suitability of certification depends on the organization’s activities, the personal information it processes and the scope established for its Privacy Information Management System.
Why Is Privacy Certification Relevant to Marina Bay?
Marina Bay is part of Singapore’s wider financial and commercial ecosystem. Businesses operating in this environment may work with international clients, regional offices, external technology providers and suppliers that expect clearly defined privacy practices.
ISO/IEC 27701:2025 offers a structured way to address these expectations through documented responsibilities, risk management and systematic oversight of personal information.
Managing Privacy Across Regional Operations
A company headquartered in Marina Bay may oversee teams, service providers and customers across several countries. Different jurisdictions can impose different requirements for collecting, retaining, sharing and transferring personal information.
A PIMS establishes a consistent management framework for identifying privacy responsibilities across these operations. Organizations must still assess the specific laws that apply in each jurisdiction.
Establishing Accountability for Data Processing
Personal information may pass between sales teams, customer service departments, HR systems, cloud platforms and external processors. Without clearly assigned responsibilities, organizations can struggle to maintain consistent oversight.
A privacy management framework helps define ownership, establish documented processes and create evidence of how privacy responsibilities are managed.
Responding to Enterprise Procurement Requirements
Large customers and business partners may request information about a supplier’s privacy controls before approving a contract. Certification can provide evidence that an independent body has assessed the organization’s PIMS for conformity.
Whether Certification is accepted as a contractual requirement depends on the customer’s procurement criteria and the certificate’s scope.
Aligning Privacy Management With Business Change
New digital products, artificial intelligence applications, customer platforms and outsourcing arrangements can change how personal information is used. A formal management system gives organizations a repeatable approach to evaluating privacy implications and reviewing relevant controls as operations evolve.
Benefits of ISO/IEC 27701:2025 Certification in Marina Bay
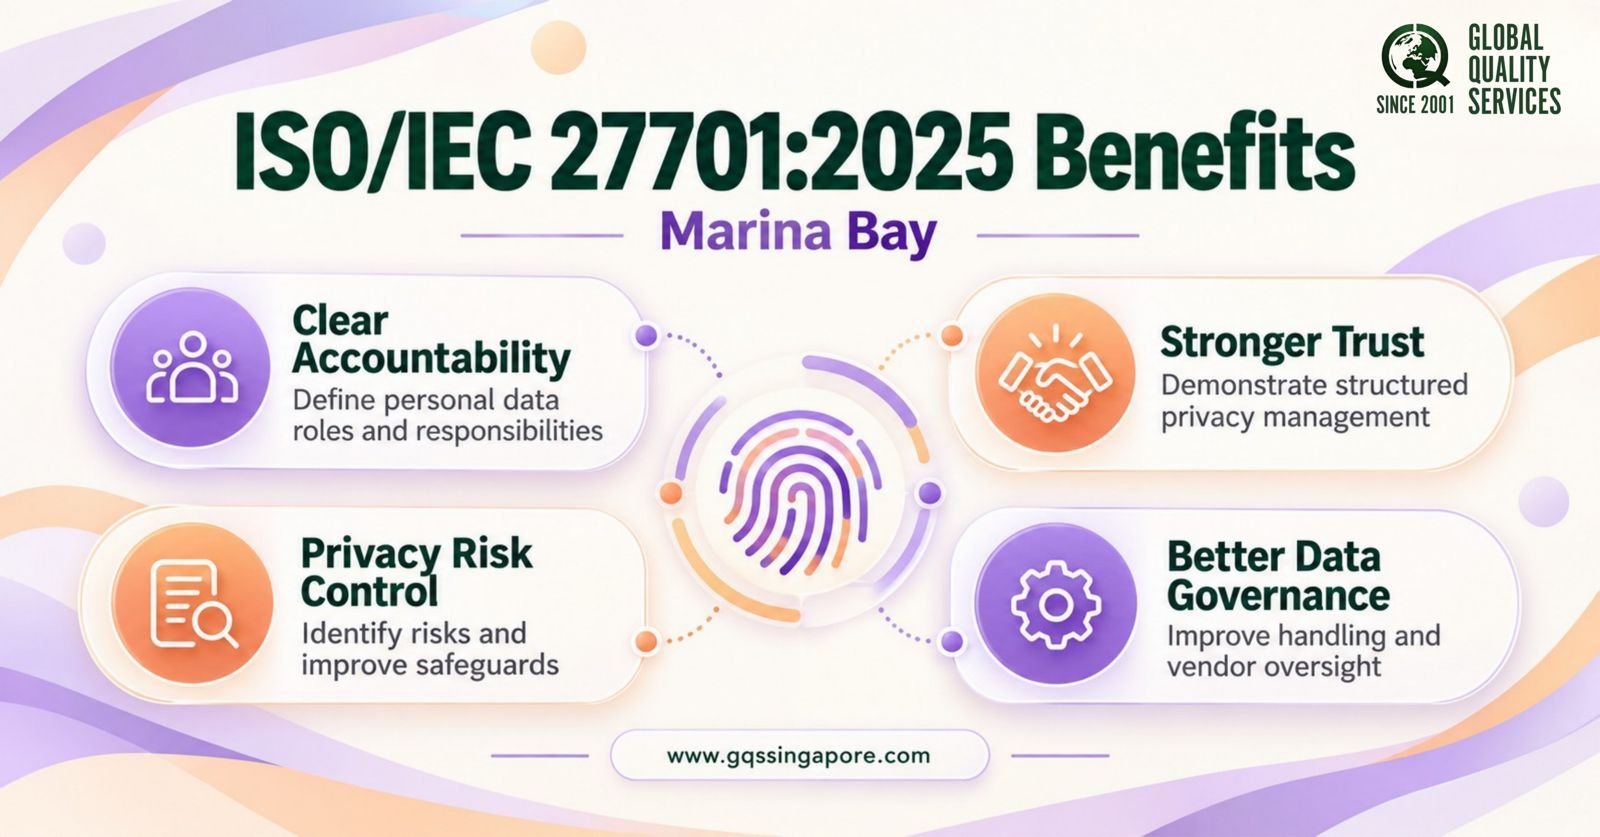
Beyond establishing a formal privacy framework, ISO/IEC 27701:2025 Certification can deliver operational and commercial value for businesses that manage personal information.
More Consistent Privacy Practices Across Departments
A documented PIMS helps bring privacy responsibilities into a common framework. Departments can work with clearer expectations for handling personal information, maintaining records, and escalating privacy-related issues.
Improved Visibility Into Personal Data Risks
Organizations can use a structured approach to identify where personal information is processed, who is responsible for it, and which activities may require additional controls. This supports more informed decisions about how to treat privacy risks.
Stronger Evidence for Client Assessments
Certification can provide objective evidence for customers, partners, and procurement teams evaluating an organization’s privacy management arrangements. It can reduce reliance on general statements about privacy commitments, although individual customers may request additional evidence.
Better Oversight of External Data Processors
Businesses often rely on software vendors, outsourced service providers, and cloud platforms. Defined privacy responsibilities and supplier oversight processes can help organizations evaluate these relationships and manage associated risks.
Support for International Expansion
A recognized privacy management framework can strengthen an organization’s approach to privacy governance when entering new markets or working with international customers. It does not replace local legal assessments, but it can provide a consistent starting point for managing privacy responsibilities.
A Foundation for Continual Management System Improvement
Certification establishes an assessment-based approach to privacy management. Reviews, corrective actions, and applicable follow-up audits can help organizations evaluate whether their arrangements remain effective as business processes and risks change.
Key Areas Covered by ISO/IEC 27701:2025
The requirements that apply to an organization depend on its role in processing personal information, its activities, and the scope of its PIMS. The standard provides a framework for addressing privacy management at both organizational and operational levels.
Leadership and Privacy Governance
Organizations need to establish relevant management system responsibilities, determine the context in which the PIMS operates, and define appropriate objectives and accountability arrangements.
Personal Information Processing Responsibilities
Businesses must consider how their activities involve personally identifiable information and establish appropriate processes to manage the associated responsibilities.
Privacy Risk Assessment and Treatment
The organization evaluates relevant privacy risks and determines appropriate measures for addressing them. The approach should reflect the nature of the processing, the organization’s responsibilities and its established management system.
Operational Controls and Documented Information
Policies, procedures, and records provide evidence that the PIMS is established and maintained. The applicable documentation depends on theorganization’ss context and the requirements relevant to its scope.
Performance Evaluation and Improvement
Monitoring, internal evaluation, management review and corrective action form part of maintaining an effective management system. These activities help identify shortcomings and determine where changes are necessary.
How to Prepare for ISO/IEC 27701:2025 Certification in Marina Bay
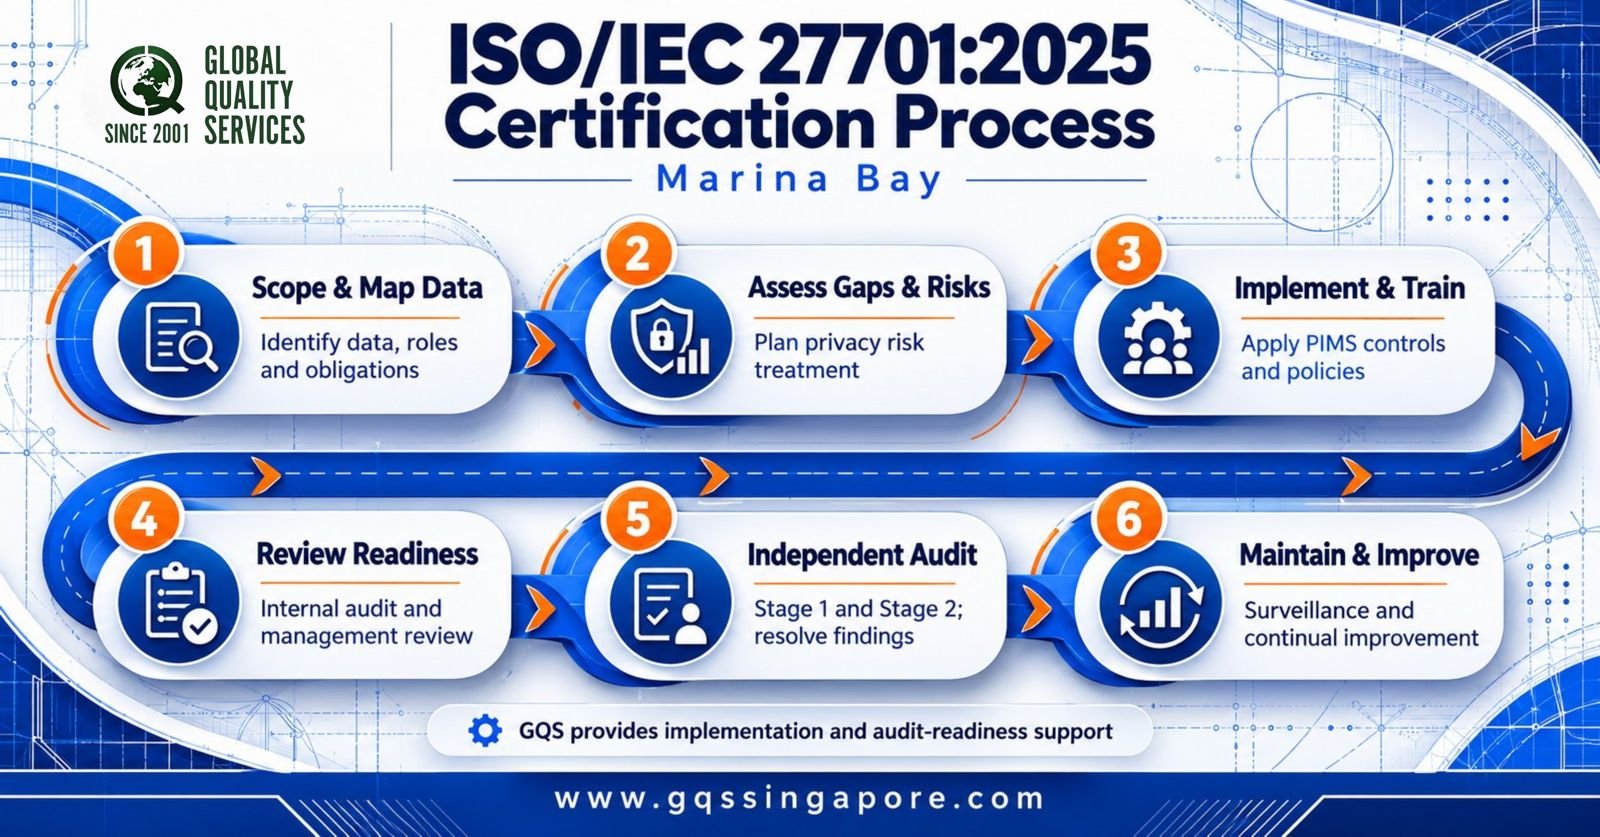
Preparation begins with understanding the organization’s current privacy management arrangements and determining how they align with the standard.
Define the Business and Certification Scope
Identify the services, departments, locations, and personal information processing activities to be included. For regional headquarters, the scope should clearly distinguish the operations covered from activities outside the proposed certification boundary.
Review Existing Privacy Processes
Examine current policies, processing records, privacy risk assessments, supplier arrangements, data retention practices, and assigned responsibilities. This review helps identify gaps that need to be addressed before the certification audit.
Establish Objective Evidence
Organizations should maintain records that show how their PIMS operates. Evidence may include approved policies, risk assessment records, internal review results, supplier-related documentation, and corrective action records, where applicable.
Evaluate Applicable Legal and Contractual Requirements
Identify the privacy laws, customer commitments, and contractual obligations relevant to the organization’s activities. Businesses handling personal information across borders should consider requirements in each relevant jurisdiction.
Arrange the Certification Assessment
Once the management system is ready, the organization can discuss its proposed scope and assessment arrangements with Global Quality Services. The audit evaluates conformity with applicable requirements, and Global Quality Services grants certification only after the relevant requirements and certification decision process are satisfied.
ISO/IEC 27701:2025 and Singapore’s Privacy Requirements
Businesses in Marina Bay should consider ISO/IEC 27701:2025 alongside the Personal Data Protection Act 2012 (PDPA), which governs how organizations handle personal data within its scope, subject to applicable provisions and exceptions.
The PDPA sets out obligations on consent, purpose limitation, protection, retention, access and correction, and transfers of personal data outside Singapore.
ISO/IEC 27701:2025 provides a management system framework for organizing privacy responsibilities and evaluating the effectiveness of relevant processes. Certification does not automatically establish compliance with every requirement of the PDPA or other applicable privacy laws.
Organizations should identify their specific legal obligations and ensure that their privacy management arrangements address the requirements relevant to their operations.
ISO/IEC 27701:2019 and ISO/IEC 27701:2025: What Should Existing Certificate Holders Consider?
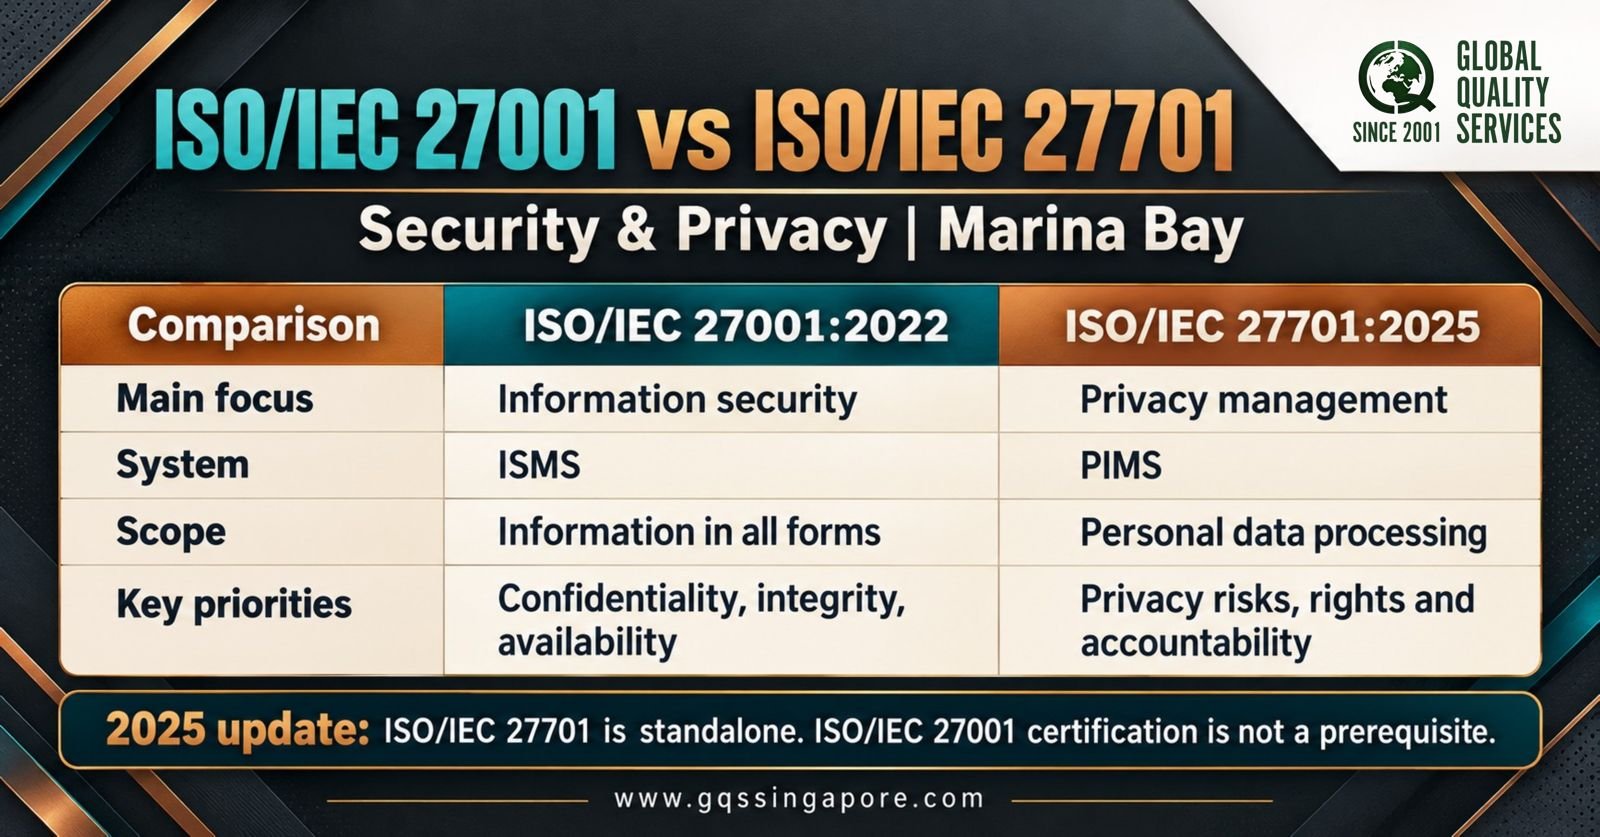
The 2025 edition introduces a key structural change: ISO/IEC 27701 is now a standalone management system standard, no longer an extension dependent on ISO/IEC 27001.
Organizations previously certified to ISO/IEC 27701:2019 should review their existing documentation, management system arrangements and certification status against the newer edition.
Key considerations include:
- Certification scope: Confirm whether the existing scope accurately reflects current business operations and personal information processing activities.
- Management system requirements: Evaluate the 2025 edition’s requirements and identify any changes needed to existing arrangements.
- Existing ISO/IEC 27001 certification: Determine how the organization’s information security management system relates to its privacy management arrangements without assuming that one certificate automatically covers the other.
- Transition or recertification arrangements: Confirm applicable deadlines, audit requirements and certification procedures with the relevant certification provider.
Organizations should base transition planning on the applicable certification and accreditation requirements rather than assume a universal transition timeline.
ISO/IEC 27701:2025 Certification With Global Quality Services in Marina Bay
Global Quality Services provides certification services for organizations seeking to demonstrate conformity with applicable management system standards.
For businesses in Marina Bay, the certification engagement should reflect the organization’s operational structure, privacy management responsibilities and proposed certification scope. This is particularly relevant for regional headquarters, financial services firms and technology companies that manage personal information across multiple business functions.
Organizations can discuss their current management system, existing certifications, operational boundaries and certification requirements with Global Quality Services before arranging an assessment.
Contact Global Quality Services to discuss ISO/IEC 27701:2025 Certification in Marina Bay, Singapore, and determine the appropriate certification scope for your business.
Frequently Asked Questions
1. Can our Marina Bay headquarters include regional offices in one ISO/IEC 27701:2025 certificate?
Potentially, yes. Multiple locations may be included where the certification scope and applicable certification arrangements permit it. The organization should identify the functions, locations, and processing activities covered, including how responsibilities are managed across regional offices. The final scope is subject to assessment and the applicable certification requirements.
2. What records should we prepare before an ISO/IEC 27701:2025 certification audit?
Preparation depends on the organization’s scope and existing PIMS. Relevant evidence may include privacy policies, personal information processing records, risk assessments, assigned responsibilities, supplier agreements, internal audit results, management review records, and corrective action documentation. The assessment will determine which evidence applies to the requirements being evaluated.
3. Can a Marina Bay company use ISO/IEC 27701:2025 to demonstrate privacy controls to enterprise customers?
Yes. A valid certificate can show that the organization’s PIMS has been assessed against ISO/IEC 27701:2025 within the stated scope. However, customers may still request security questionnaires, contractual assurances, technical evidence, or additional assessments depending on the nature of the services and their own requirements.
4. Does ISO/IEC 27701:2025 certification cover personal data used in artificial intelligence systems?
The standard can be relevant to organizations that process personal information through AI-enabled products and services. The assessment should consider the processing activities and privacy responsibilities within scope. Certification does not automatically establish that an AI system is safe, unbiased, or compliant with every applicable AI and data protection requirement.
5. What should we check before selecting an ISO/IEC 27701:2025 certification provider in Singapore?
Check the provider’s competence,applicable certification and accreditation arrangements, scope of services offered, audit methodology,y and certificate verification procedures. If accreditation is important to a customer or tender, confirm that the relevant accreditation covers ISO/IEC 27701:2025 and the proposed scope rather than relying solely on a general accreditation claim.