
For SaaS companies, winning enterprise customers often depends on more than delivering a reliable product. Customers also want confidence that their sensitive information is protected and their security risks are properly managed. According to Verizon’s 2026 Data Breach Investigations Report, 31% of data breaches began with the exploitation of software vulnerabilities, making it the leading initial access method.
This finding highlights why strong security controls and regular reviews matter for businesses that manage customer data. SOC 2 readiness helps SaaS companies prepare to demonstrate how they manage security and other relevant risks. However, preparation involves more than creating policies or installing security tools.
Businesses need clearly defined controls, reliable evidence, and consistent practices. This guide explains the SOC 2 readiness process, common gaps, preparation timelines, and how SaaS companies can prepare for an independent examination.
Why SOC 2 Matters for SaaS Startups
SOC 2 evaluates how service organizations manage customer data based on five Trust Services Criteria: Security (mandatory), Availability, Processing Integrity, Confidentiality, and Privacy. Unlike prescriptive standards, SOC 2 is flexible, allowing you to tailor controls to your business model.
Companies that achieve SOC 2 unlock enterprise contracts, streamline vendor due diligence, and strengthen actual security posture—reducing breach risk while meeting customer expectations.
Understanding the Five Trust Services Criteria
Every SOC 2 assessment evaluates your organization against specific Trust Services Criteria established by the American Institute of Certified Public Accountants. You choose which criteria apply to your software architecture during scoping:
- Security: Protection of system resources against unauthorized access, malicious breaches, and data theft. This criterion is mandatory for every SOC 2 report.
- Availability: Ensuring your application remains operational and accessible to customers in accordance with your service level agreements.
- Processing Integrity: Guaranteeing that system data processing remains complete, valid, accurate, and authorized at all times.
- Confidentiality: Safeguarding sensitive business data throughout storage, transmission, and internal handling.
- Privacy: Managing personally identifiable information according to your published privacy policies and regulatory obligations.
The SOC 2 Readiness Checklist
Readiness means having controls designed, implemented, documented, and operating before your formal audit begins. Here’s what you need to prepare:
1. Define Your Audit Scope
Identify which Trust Services Criteria apply to your business beyond the mandatory Security criterion. SaaS companies offering uptime guarantees should include Availability, while those processing sensitive transactions need Processing Integrity. Document which systems, applications, infrastructure, and personnel fall within scope. Cloud-hosted SaaS platforms typically include production environments, development systems, administrative access, and third-party integrations.
2. Establish Core Security Policies
SOC 2 requires documented policies governing information security, access control, change management, incident response, business continuity, and vendor management. These aren’t checkbox exercises—auditors verify employees actually follow them. Critical policies include:
- Information Security Policy
- Acceptable Use Policy
- Access Control Policy
- Incident Response Plan
- Business Continuity and Disaster Recovery Plan
- Vendor Management Policy
3. Implement Technical Controls
- Access Management: Multi-factor authentication for all systems, role-based access control, quarterly access reviews, immediate deprovisioning for departing employees.
- Logging and Monitoring: Centralized logging for authentication, system changes, and administrative actions. Configure alerts for suspicious activities and retain logs for one year minimum.
- Encryption: Use TLS 1.2+ for data in transit and industry-standard encryption for data at rest. Document encryption methods and key management.
- Vulnerability Management: Monthly vulnerability scans, annual penetration testing, documented patch management for critical vulnerabilities.
- Change Management: Document and approve production changes, maintain change logs, implement rollback procedures, separate development and production environments.
4. Vendor Risk Management
With 84% of companies using SaaS applications that experienced breaches, your security depends on vendor choices. Maintain a vendor inventory, review critical vendors’ SOC 2 reports or security documentation, document evaluation processes, and include security requirements in contracts. Auditors verify systematic third-party risk management.
5. Business Continuity and Disaster Recovery
Implement regular automated backups, documented recovery procedures, and tested restoration processes. Define Recovery Time Objectives and Recovery Point Objectives. Test backups regularly—untested backups aren’t backups. Document disaster recovery plans and conduct annual testing.
6. Employee Security Awareness
With 95% of breaches involving human error, training is critical. Implement security training covering password management, phishing, data handling, and incident reporting. Train new hires within their first week and provide annual refreshers. Document training activities and maintain completion records for auditor review.
7. Documentation and Evidence Collection
Start collecting evidence immediately: access review reports, change management tickets, vulnerability scan results, security training certificates, incident response records, backup test results, and vendor assessments. Organize evidence systematically by control area. Many companies use GRC platforms to automate collection and centralize documentation.
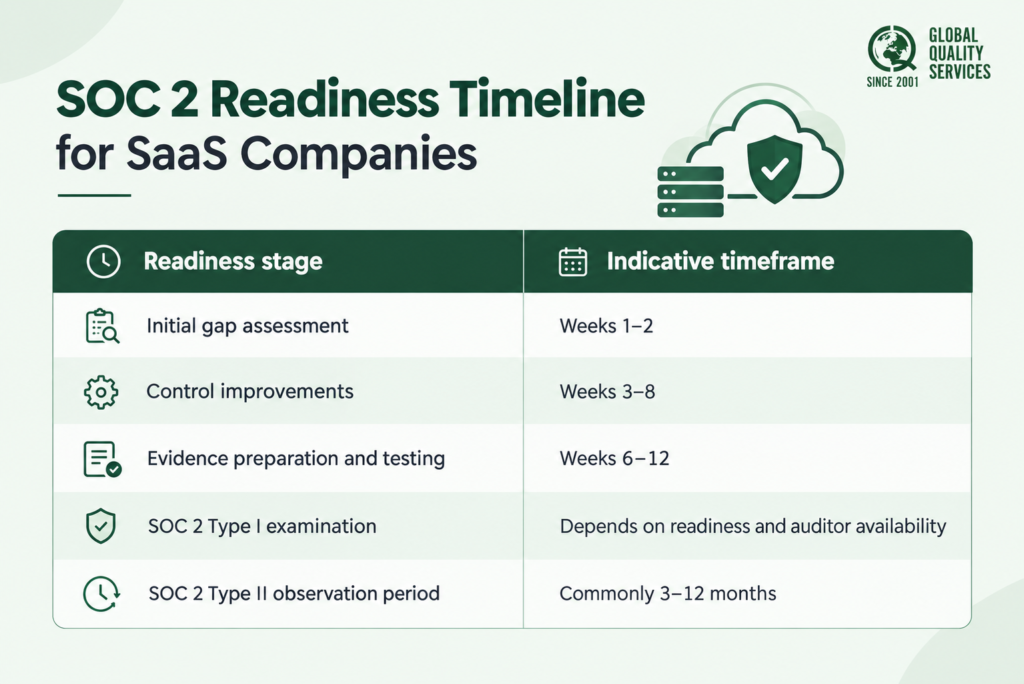
SOC 2 Readiness Timeline for SaaS Companies
The time needed to prepare for SOC 2 varies depending on the company’s existing security controls, infrastructure, team size, and the reasons for the examination. Generally speaking, a company with established security practices may require less preparation than a startup with a developing compliance program.
Common SOC 2 Readiness Gaps in SaaS Companies
SaaS companies may already have security policies, cloud infrastructure controls, and access management systems in place before starting SOC 2 preparation. However, these measures do not automatically make a company ready for a SOC 2 examination. Businesses must also demonstrate that their controls are properly implemented, consistently followed, and supported by reliable evidence. Here are some common gaps SaaS companies should address before an examination:
- Incomplete system scope: Applications, cloud environments, integrations, or support systems handling customer data may be overlooked.
- Weak access management: Employees may retain unnecessary permissions, or access reviews may not be documented.
- Missing audit evidence: Records of approvals, security reviews, and other control activities may be incomplete.
- Inconsistent change management: Software updates may lack documented testing, approvals, or appropriate reviews.
- Unclear vendor responsibilities: Security responsibilities shared with cloud providers and other third parties may not be clearly documented.
- Unresolved security risks: Vulnerabilities and identified weaknesses may remain open without clear ownership or corrective action.
- Untested incident response plans: Response procedures may exist but lack evidence of testing or periodic review.
Why Choose Global Quality Services for SOC 2 Readiness in Singapore?
Choosing the right consultant can help your SaaS business understand its compliance requirements and prepare for enterprise customer security reviews. Global Quality Services (GQS) brings established certification consulting experience and a practical approach to helping organisations manage compliance requirements:
- 26+ years of consulting experience: Benefit from GQS’s extensive background in certification consulting and management system compliance.
- Cross-industry experience: Gain guidance informed by experience working with organisations across different sectors and business environments.
- Business-focused recommendations: Receive guidance suited to your organisation’s existing processes, resources, and compliance objectives.
- Experienced consulting team: Work with consultants who understand documentation, training, audit preparation, and compliance management.
- International consulting presence: Access support from a firm serving organisations across multiple markets.
- Focus on sustainable compliance: Build an understanding of the controls and documentation needed to support ongoing compliance, rather than treating preparation as a one-time task.
Accelerate Your SOC 2 Compliance Journey With Global Quality Services
Preparing for a system audit without structured guidance often drains internal engineering resources and delays sales pipelines. Global Quality Services helps technology providers streamline their security frameworks, eliminate compliance gaps, and secure enterprise contracts faster. Contact our advisory team today to schedule your initial readiness assessment.
Frequently Asked Questions
1. How long does SOC 2 readiness take?
Preparation typically requires 3-6 months for organizations starting from scratch, depending on existing security maturity. Companies with strong security foundations may achieve readiness faster, while those requiring significant control implementation need longer preparation periods.
2. Can we achieve SOC 2 without consultants?
Yes, particularly if you have internal security and compliance expertise. However, first-time implementations benefit significantly from consultant guidance to avoid common pitfalls and accelerate timelines. Many companies use consultants for initial readiness and handle maintenance internally.
3. What’s the difference between SOC 2 and ISO 27001?
ISO 27001 is an international standard for information security management systems, while SOC 2 is a US-based auditing framework. ISO 27001 provides certification, whereas SOC 2 produces an attestation report. Many companies pursue both—there’s significant overlap in control requirements.
4. Do Singapore companies need SOC 2?
SOC 2 isn’t legally required in Singapore, but it’s essential for SaaS companies selling to US enterprises or multinational corporations. Many Singapore-based companies pursue SOC 2 to access international markets and demonstrate world-class security practices.
5. What happens if we fail the SOC 2 audit?
SOC 2 doesn’t have traditional pass/fail outcomes. If controls don’t meet requirements, auditors document exceptions in the report. Significant exceptions may result in qualified opinions, impacting customer trust. Work with your auditor to remediate issues before report finalization.