Technology firms and corporate offices in Changi Business Park often rely on cloud platforms to store and process customer information. This makes personal data protection an important part of daily business operations. Singapore’s Cyber Security Agency reported that 284,300 systems in Singapore were infected with malware in 2025, more than double the previous year’s figure.
ISO 27018 helps organizations protect personally identifiable information handled through public cloud services. If your company manages sensitive customer data, an experienced consultant such as Global Quality Services can help you understand the standard and prepare for certification.
What is ISO 27018 Certification
ISO 27018 is an international standard that focuses on protecting personally identifiable information (PII) in public cloud environments. It gives cloud service providers clear guidance on how to handle customer data responsibly. The standard covers important privacy practices, including data access, consent, disclosure, retention, and secure deletion.
It also complements ISO 27001 by adding privacy-focused controls for cloud-based data processing. For businesses that store or process customer information through cloud services, ISO 27018 certification demonstrates a serious commitment to data privacy and responsible information handling.
Why Do Businesses in Changi Business Park Need ISO 27018 Certification?
Changi Business Park hosts companies across technology, finance, logistics, professional services, and other business sectors. Many organizations in this area depend on cloud applications, digital records, and third-party technology providers to run their operations.
These systems often handle employee details, customer records, financial information, and other personal data. A weak privacy practice can affect customer confidence and business relationships.
ISO 27018 helps organizations address these concerns in several ways.
1. Protect Customer Information Stored in the Cloud
Businesses use cloud platforms to manage customer profiles, employee records, and other personal information. ISO 27018 helps establish clear privacy controls for handling this data and restricting unauthorized access.
2. Demonstrate Responsible Data Handling
Customers want to understand how service providers collect, use, store, and disclose their information. ISO 27018 gives organizations a recognized basis for explaining their cloud privacy practices.
3. Improve Privacy Management Across Cloud Services
The standard addresses specific responsibilities related to data access, retention, disclosure, and deletion. These controls help businesses manage personal information more consistently.
4. Support Singapore’s Data Protection Requirements
Organizations in Singapore must consider their responsibilities under the Personal Data Protection Act (PDPA). ISO 27018 can support stronger internal privacy practices, although certification does not automatically establish compliance with the PDPA.
5. Strengthen Business Credentials
Enterprise customers may review privacy and information security practices before choosing a technology partner. ISO 27018 certification can give your business additional evidence of its approach to protecting personal information.
Key ISO 27018 Requirements for Businesses in Changi Business Park
Organizations pursuing ISO 27018 certification must address privacy controls that apply to their public cloud data processing activities.
The following areas require attention:
1. Purpose and Consent for Data Processing
Establish clear rules for processing personal information. Your organization should use customer data for agreed purposes and follow applicable contractual and legal obligations.
2. Access to Personal Information
Restrict access to sensitive information based on job responsibilities. Maintain suitable access management procedures and allow only authorized personnel to handle customer records.
3. Data Disclosure and Sharing
Define how your organization shares personal information with third parties. Maintain appropriate records and follow contractual requirements when disclosing customer data.
4. Data Retention and Secure Deletion
Set clear retention periods for personal information. Establish procedures to return or securely delete data when your organization no longer needs it.
5. Personal Data Breach Management
Prepare procedures to identify, report, and respond to personal data breaches. Assign responsibilities and establish suitable communication and incident response arrangements.
6. Privacy Transparency and Accountability
Explain your organization’s privacy practices to relevant customers and stakeholders. Maintain records that show how your business handles personal information.
7. Information Security Measures
Apply suitable security controls to protect personal information against unauthorized access, accidental loss, alteration, or disclosure.
ISO 27018 Certification Process in Changi Business Park
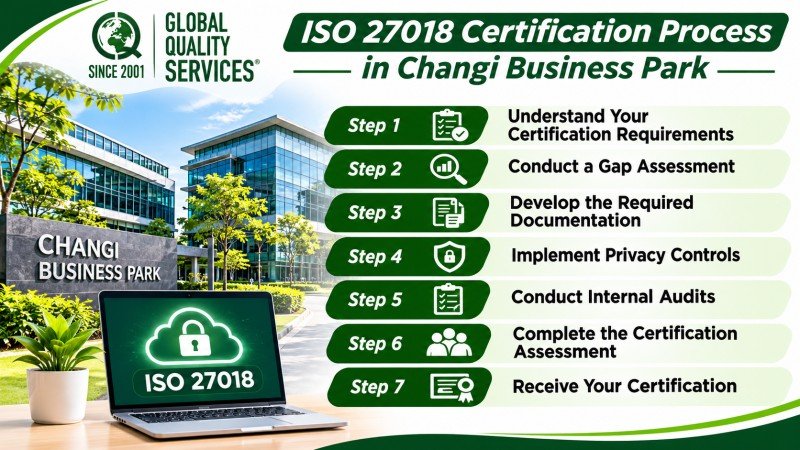
Preparing for ISO 27018 certification involves reviewing existing privacy practices, addressing gaps, and checking whether the controls work in daily operations.
Global Quality Services can guide your organization through the following stages.
Step 1: Understand Your Certification Requirements
Our consultants discuss your cloud services, business activities, customer expectations, and data processing responsibilities. This helps identify the appropriate certification scope.
Step 2: Conduct a Gap Assessment
We examine your current information security and privacy practices against the relevant ISO 27018 requirements. This review highlights missing controls and areas that need improvement.
Step 3: Develop the Required Documentation
Your organization prepares relevant policies, procedures, records, and privacy controls. Our consultants help create documentation that reflects your actual cloud services and business activities.
Step 4: Implement Privacy Controls
We guide your team in addressing identified gaps. This may include improving access restrictions, data handling procedures, retention practices, deletion controls, and incident response arrangements.
Step 5: Conduct Internal Audits
Your organization reviews the implemented controls through internal audits. This helps identify outstanding issues and gives your team time to address them before the external assessment.
Step 6: Complete the Certification Assessment
An independent certification body evaluates your management system and relevant controls. Your organization must address any nonconformities raised during the assessment.
Step 7: Receive Your Certification
Once your organization meets the certification body’s requirements, it can receive the ISO 27018 certificate. Your team must continue reviewing its privacy controls and meeting applicable surveillance requirements.
How Global Quality Services Experts Help You with ISO 27018 Certification in Changi Business Park
Global Quality Services is a reputed consultant supporting businesses with international ISO certification requirements. Our team brings expertise in information security, cloud privacy, and management system consulting. We offer practical guidance, customized documentation support, employee training, and audit preparation.
With experience across different industries and international markets, we help organizations address ISO 27018 requirements while keeping their business needs and certification goals in focus.
Choose Global Quality Services for ISO 27018 Certification in Changi Business Park
Your customers trust your organization to handle their personal information responsibly. Strong cloud privacy practices can help protect that trust and support lasting business relationships.
Global Quality Services offers ISO 27018 consulting support for businesses in Changi Business Park. Our team can help you review your existing practices, identify gaps, prepare documentation, and get ready for the independent certification assessment.
Contact Global Quality Services today to discuss your certification scope and request a consultation. Let our consultants help you prepare for ISO 27018 certification with a plan that suits your business.
Frequently Asked Questions
1. Is ISO 27018 relevant to companies using Microsoft Azure or Amazon Web Services?
Yes. ISO 27018 applies to public cloud environments where organizations process personal information. Its relevance depends on the services offered and the company’s role in data processing.
2. Can a business pursue ISO 27018 without ISO 27001?
ISO 27018 complements ISO 27001 and is generally assessed alongside an appropriate information security management system. Discuss the applicable certification arrangement with your certification body.
3. Does ISO 27018 certification help with customer security assessments?
Yes. It gives customers documented evidence of your cloud privacy practices and can support vendor reviews, procurement discussions, and contractual assessments.
4. How often should a company review its ISO 27018 controls?
Review your controls regularly and whenever your cloud services, business activities, risks, or applicable requirements change. Certification bodies also conduct periodic surveillance assessments.
5. Can Global Quality Services help businesses using multiple cloud platforms?
Global Quality Services can discuss your cloud environment and consulting requirements, then guide your team in addressing relevant privacy controls across its services.