Technology companies in One-North often handle customer records and personal information through cloud services. Protecting this data takes more than basic security measures. The Straits Times reported that Singapore detected 284,300 malware-infected systems in 2025, more than double the previous year’s figure.
ISO 27018 helps organizations protect personally identifiable information stored in public cloud environments. If your business handles sensitive customer data, certification can strengthen your privacy practices. An experienced consultant such as Global Quality Services can guide your team through the requirements and certification preparation.
What is ISO 27018 Certification
ISO/IEC 27018 is an international standard that focuses on protecting personally identifiable information (PII) in public cloud environments. It gives cloud service providers specific guidance on handling personal data responsibly.
The standard addresses privacy risks that arise when organizations process personal information on behalf of their customers. It covers areas such as data access, consent, disclosure, retention, deletion, and transparency.
ISO 27018 works alongside ISO 27001 and its information security controls. It adds privacy-focused requirements for organizations acting as PII processors in public cloud environments.
For businesses in One-North, this standard is particularly relevant to:
- Cloud service providers
- SaaS companies
- IT service providers
- Data hosting companies
- Technology and software development firms
- Organizations processing personal information through cloud platforms
- Businesses managing cloud-based customer records
By pursuing ISO 27018 certification, organizations can demonstrate their commitment to responsible personal data processing and stronger cloud privacy practices.
Why Do Businesses in One-North Need ISO 27018 Certification?
One-North has developed into an important business and research hub in Singapore. Its ecosystem includes technology companies, biomedical organizations, research institutions, and startups. JTC identifies eight distinct precincts within One-North, supporting different industries and business activities.
This business environment creates a strong need for responsible data handling. Companies regularly exchange sensitive information with customers, suppliers, research partners, and cloud service providers.
ISO 27018 certification can help businesses address these concerns.
1. Protect Personal Information in Cloud Environments
Cloud platforms often store customer information, employee records, and other sensitive data. ISO 27018 helps organizations establish privacy controls for handling this information and preventing unauthorized access.
2. Build Stronger Client Relationships
Enterprise customers want to know how their service providers handle personal information. ISO 27018 gives businesses a recognized way to demonstrate their privacy practices during vendor assessments and partnership discussions.
3. Strengthen Cloud Privacy Controls
The standard addresses specific privacy responsibilities for cloud-based data processing. It helps organizations establish clear rules for data access, disclosure, retention, and deletion.
4. Support Regulatory Compliance
Organizations operating in Singapore must consider applicable privacy requirements under the Personal Data Protection Act (PDPA). ISO 27018 can support these efforts by strengthening internal privacy practices. However, certification does not automatically establish PDPA compliance.
5. Improve Business Opportunities
Some enterprise customers consider independent security and privacy certifications when selecting cloud service providers. ISO 27018 certification can strengthen your company’s credentials during procurement and business negotiations.
Key ISO 27018 Requirements for Businesses in One-North
Organizations pursuing ISO 27018 certification must address privacy controls relevant to their role as cloud-based PII processors.
The following areas deserve particular attention:
1. Consent and Purpose of Data Processing
Organizations must establish clear rules for processing personal information. They should use customer data only for agreed purposes and follow applicable contractual and legal requirements.
2. Personal Data Access Control
Businesses must restrict access to personal information. Only authorized personnel should access customer records, and organizations should maintain appropriate access management procedures.
3. Data Disclosure and Transfer
Cloud service providers must establish controls for sharing personal information with third parties. They should maintain transparency about disclosures and follow contractual obligations.
4. Data Retention and Deletion
Organizations should define how long they retain personal information. They must also establish procedures for securely deleting or returning data when retention is no longer necessary.
5. Data Breach Management
Companies must establish procedures to identify, report, and manage personal data breaches. These procedures should define responsibilities, communication channels, and incident response activities.
6. Transparency and Accountability
Cloud service providers should communicate their privacy practices clearly. They must also maintain records that demonstrate how they handle and protect personal information.
7. Information Security Controls
Organizations must apply suitable security measures to protect personal information against unauthorized access, accidental loss, alteration, and disclosure.
ISO 27018 Certification Process in One-North
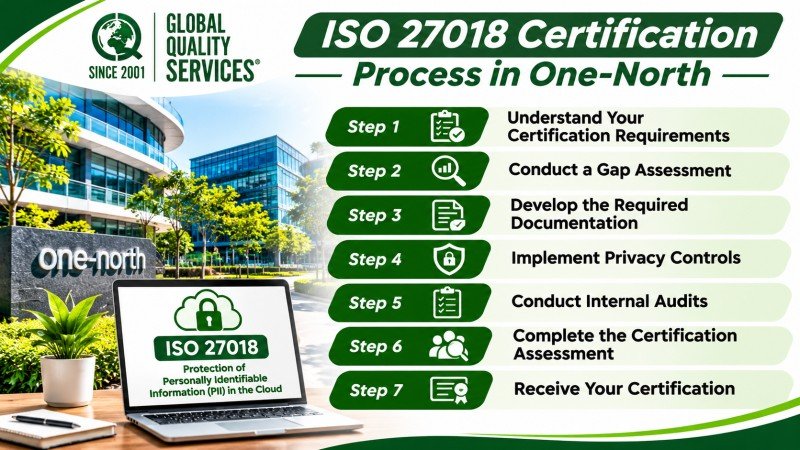
Getting ISO 27018 certified requires more than preparing policies and collecting documents. Your organization must demonstrate that its privacy controls work in practice.
Global Quality Services supports businesses through the following stages.
Step 1: Understand Your Certification Requirements
Our consultants discuss your business activities, cloud services, customer requirements, and data processing responsibilities. This helps determine the appropriate certification scope.
Step 2: Conduct a Gap Assessment
We review your existing information security and privacy practices against applicable ISO 27018 requirements. The assessment identifies missing controls and areas requiring attention.
Step 3: Develop the Required Documentation
Your organization prepares relevant policies, procedures, records, and privacy controls. Our consultants guide your team in developing documentation that reflects actual business activities.
Step 4: Implement Privacy Controls
We help your team address identified gaps and apply suitable controls. This includes access management, data handling, retention, deletion, and incident response practices.
Step 5: Conduct Internal Audits
Your organization reviews the implemented controls through internal audits. This helps identify outstanding issues before the independent certification assessment.
Step 6: Complete the Certification Assessment
An independent certification body evaluates your management system and applicable controls. Your organization must address any nonconformities identified during the assessment.
Step 7: Receive Your Certification
Once your organization meets the certification body’s requirements, it can receive the ISO 27018 certificate. Your team must continue maintaining the controls and meeting applicable surveillance requirements.
How Global Quality Services Experts Help You with ISO 27018 Certification in One-North
Selecting the right consultant can make a significant difference to your certification experience. You need a reputed consultant who understands information security, cloud privacy, and the practical challenges businesses face.
Global Quality Services brings experience in international management system consulting, certification support, and compliance services. Our Singapore-based consulting operations support organizations across different industries and business locations.
Our published company profile highlights our work in ISO certification, SOC 2, PCI DSS, and other compliance areas. The company’s consulting leadership also includes Singapore Certified Management Consultant expertise and TÜV SÜD-certified ISO 27001 auditing experience.
Why businesses choose Global Quality Services:
- Reputed consultant for international ISO certification requirements
- Singapore Certified Management Consultant expertise
- TÜV SÜD-certified ISO 27001 auditing experience within the consulting leadership
- Practical understanding of information security and privacy requirements
- Experience supporting organizations across multiple industries
- Customized consulting based on business size and certification scope
- Integrated support for related ISO management system standards
- Documentation, training, implementation, and internal audit assistance
- Regional consulting experience across Singapore and other Asian markets
- Direct guidance from experienced certification consultants
- Client-focused support throughout the certification engagement
Our objective is to help your organization develop a system that meets the standard and works within its actual business operations.
Speak with Global Quality Services for ISO 27018 Certification in One-North
Your customers trust you with their personal information. Make sure your business has the right privacy controls to protect that trust. Global Quality Services offers professional ISO 27018 consulting services in One-North, covering documentation, gap assessments, implementation guidance, and audit preparation. Speak with our consultants today to discuss your certification requirements, understand the support you need, and receive a consultation tailored to your business. Contact Global Quality Services to get started.
Frequently Asked Questions
1. Is ISO 27018 certification relevant to companies using AWS, Microsoft Azure, or Google Cloud?
Yes. ISO 27018 is relevant to cloud environments where organizations process personal information. Its applicability depends on the company’s role, services, and certification scope.
2. Can a company pursue ISO 27018 without ISO 27001 certification?
ISO 27018 is designed to complement ISO 27001. Certification arrangements generally assess it alongside an appropriate information security management system.
3. Does ISO 27018 certification help during enterprise vendor assessments?
Yes. It gives customers documented evidence of cloud privacy practices, which can support vendor evaluations, procurement discussions, and contractual security reviews.
4. How often must organizations review their ISO 27018 controls?
Organizations should review controls regularly and whenever business operations, cloud services, risks, or applicable requirements change. Certification bodies also conduct periodic surveillance assessments.
5. Can Global Quality Services support companies with multiple cloud platforms?
Yes. Global Quality Services can assess your consulting requirements across different cloud environments and help align relevant privacy controls with your business operations.