Businesses in Raffles Place handle sensitive information across financial services, investment management, corporate advisory, fintech, legal services, and regional business operations. As Singapore strengthens its focus on responsible data handling, organizations need a structured approach to manage personal information and demonstrate privacy accountability.
ISO/IEC 27701:2025 is the second edition of the international standard for Privacy Information Management Systems (PIMS). It establishes requirements for organizations that control or process personally identifiable information (PII), making it relevant to businesses that manage customer records, employee information, financial account details, and other personal data.
Global Quality Services provides ISO/IEC 27701:2025 certification services in Raffles Place, Singapore, for organizations seeking a recognized framework to manage privacy risks, strengthen internal controls, and demonstrate their commitment to protecting personal information.
ISO/IEC 27701:2025 Certification Services in Raffles Place
ISO/IEC 27701:2025 Certification enables organizations to demonstrate that their Privacy Information Management System meets the standard’s applicable requirements. It addresses how organizations collect, process, store, access, share, and manage personal information throughout its lifecycle.
For businesses operating in Raffles Place, an effective privacy management system is particularly important when handling confidential client information, outsourcing data processing, working with international partners, or managing information across multiple jurisdictions.
Global Quality Services offers certification services aligned with ISO/IEC 27701:2025, with the assessment scope determined by the organization’s activities, information processing responsibilities and applicable requirements.
Benefits of ISO/IEC 27701:2025 Certification in Raffles Place
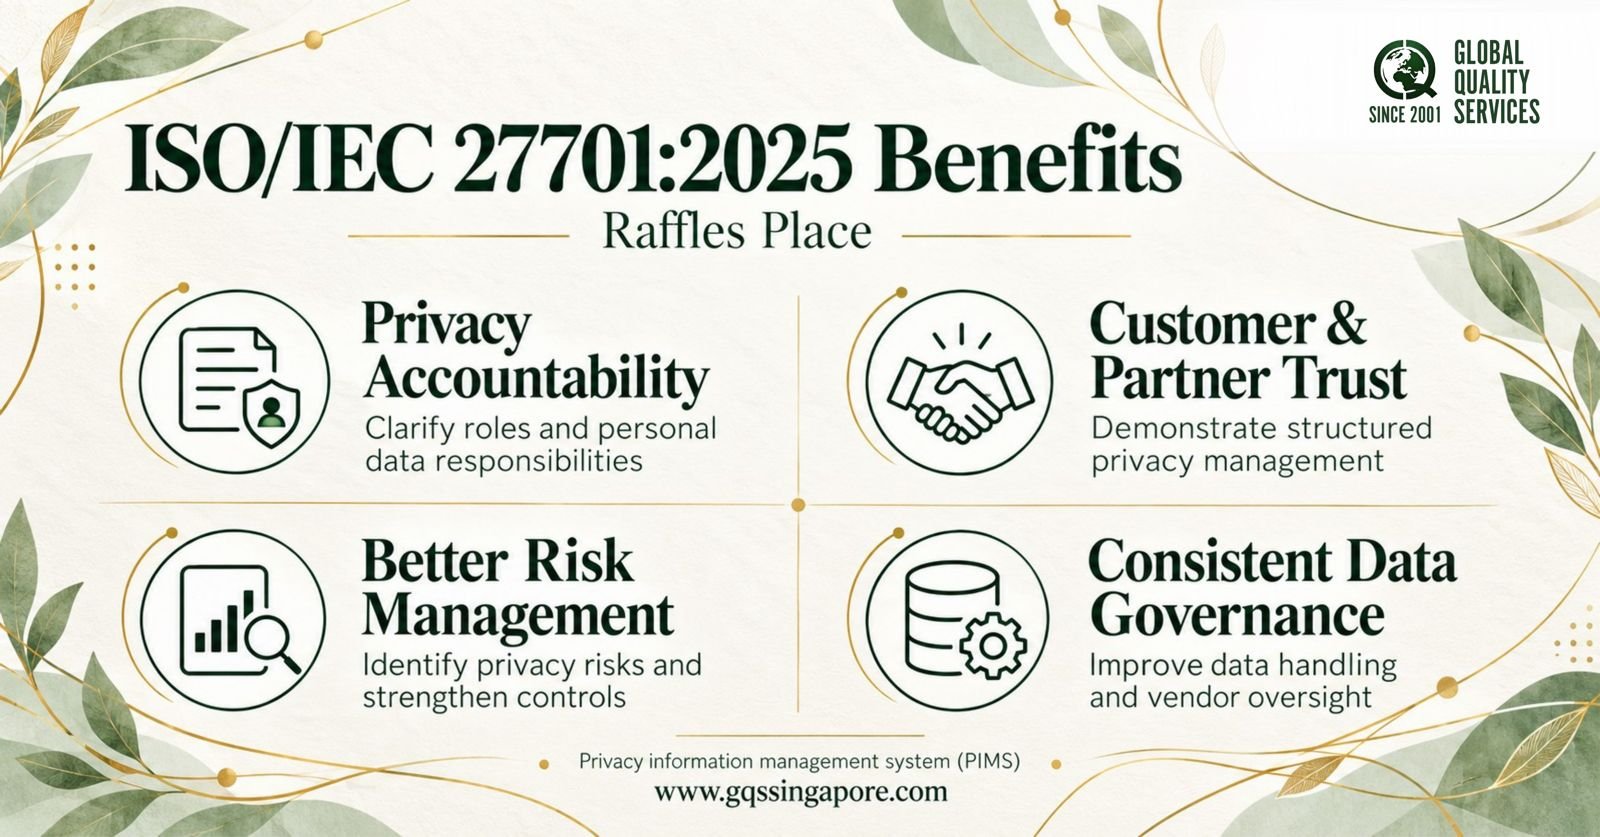
ISO/IEC 27701:2025 Certification offers practical benefits to organizations that manage personal information in their daily operations. For businesses in Raffles Place, a structured Privacy Information Management System can strengthen internal accountability and provide evidence of a consistent approach to privacy management.
1. Better Control Over Personal Information
A defined privacy management system helps organizations identify the personal information they hold, understand how it is processed, and establish appropriate controls throughout its lifecycle. This improves visibility across departments, business functions, and external service providers.
2. Stronger Client and Stakeholder Confidence
Certification provides independent evidence that an organization’s Privacy Information Management System has been assessed against ISO/IEC 27701:2025. This can be valuable when responding to client security questionnaires, vendor assessments and privacy-related procurement requirements.
3. Clearer Roles and Responsibilities
Organizations can establish clearer accountability for privacy-related decisions, data processing activities, and operational controls. Clear responsibilities can reduce confusion between internal teams and third parties handling personal information.
4. More Structured Privacy Risk Management
A systematic approach helps organizations identify privacy risks, assess their potential impact, and determine appropriate treatment measures. This helps businesses make informed decisions about data collection, access permissions, retention practices and information sharing.
5. Improved Supplier and Third-Party Oversight
Businesses that depend on cloud platforms, outsourced operations, or external data processors can use their privacy management framework to set expectations and assess relevant risks. This is particularly useful when personal information moves between different service providers or business locations.
6. Support for Business Growth and Tender Opportunities
A recognized privacy management certification can strengthen an organization’s credentials when pursuing enterprise contracts, strategic partnerships, or opportunities that require formal evidence of privacy controls. Acceptance depends on the customer’s specific requirements, tender conditions, and applicable contractual obligations.
7. A Framework for Continual Improvement
Certification encourages organizations to evaluate their privacy management arrangements against defined requirements and address identified gaps. Periodic reviews and surveillance activities help maintain focus on the management system’s continued effectiveness as business operations change.
Who Needs ISO/IEC 27701:2025 Certification in Raffles Place?
The standard applies to organizations of different sizes and across industries, including businesses that act as personal information controllers, processors, or both.
It can be relevant to:
- Banks and financial services firms: Organizations that handle customer identification details, account information, and financial records.
- Fintech and payment companies: Businesses processing user information, transaction-related personal data and digital account records.
- Corporate advisory and legal firms: Organizations that manage client documents, confidential communications, and employee information.
- Investment and asset management companies: Firms that maintain investor records, client profiles, and associated personal information.
- Technology and SaaS providers: Businesses processing personal data on behalf of customers under contractual arrangements.
- HR, recruitment,, and professional services firms: Organizations that handlOrganizations that handlee employment records, candidate information,, and payroll data.
The certification scope should reflect the actual services, systems, locations, and personal data processing activities covered by the organization’s Privacy Information Management System.
Why Pursue ISO/IEC 27701:2025 Certification in Raffles Place?
Raffles Place is a major commercial district in Singapore’s Central Business District, with businesses operating in highly connected financial and professional service networks. In this environment, privacy management can influence client confidence, supplier relationships, and the ability to meet contractual data protection expectations.
Strengthen Personal Data Governance
ISO/IEC 27701:2025 establishes a systematic approach to identifying privacy responsibilities, evaluating risks and maintaining controls over personal information. It helps organizations establish clearer accountability for the information they collect and process.
Demonstrate Privacy Management to Business Partners
Corporate customers, enterprise procurement teams and international partners may require evidence of formal privacy controls before entering into business relationships. Certification provides independent evidence that an organization’s privacy management system has been assessed against the standard.
Address Singapore’s Data Protection Expectations
Singapore’s Personal Data Protection Act 2012 (PDPA) sets out obligations for organizations covered by the law regarding personal data. ISO/IEC 27701:2025 can support a structured approach to managing privacy risks and documenting relevant processes.
Certification does not automatically establish compliance with every PDPA obligation or other applicable privacy law. Organizations must evaluate their legal responsibilities separately.
Improve Accountability Across Data Processing Activities
Businesses frequently share personal information with service providers, cloud platforms, outsourced teams and regional offices. A formal privacy management system helps define responsibilities and provide more consistent oversight of these arrangements.
Support International Business Relationships
Organizations in Raffles Place may work with customers and partners across Asia-Pacific, Europe and other markets. ISO/IEC 27701:2025 provides an internationally recognized framework for privacy management, although certification alone does not cover jurisdiction-specific legal requirements.
ISO/IEC 27701:2025 Certification Process in Raffles Place
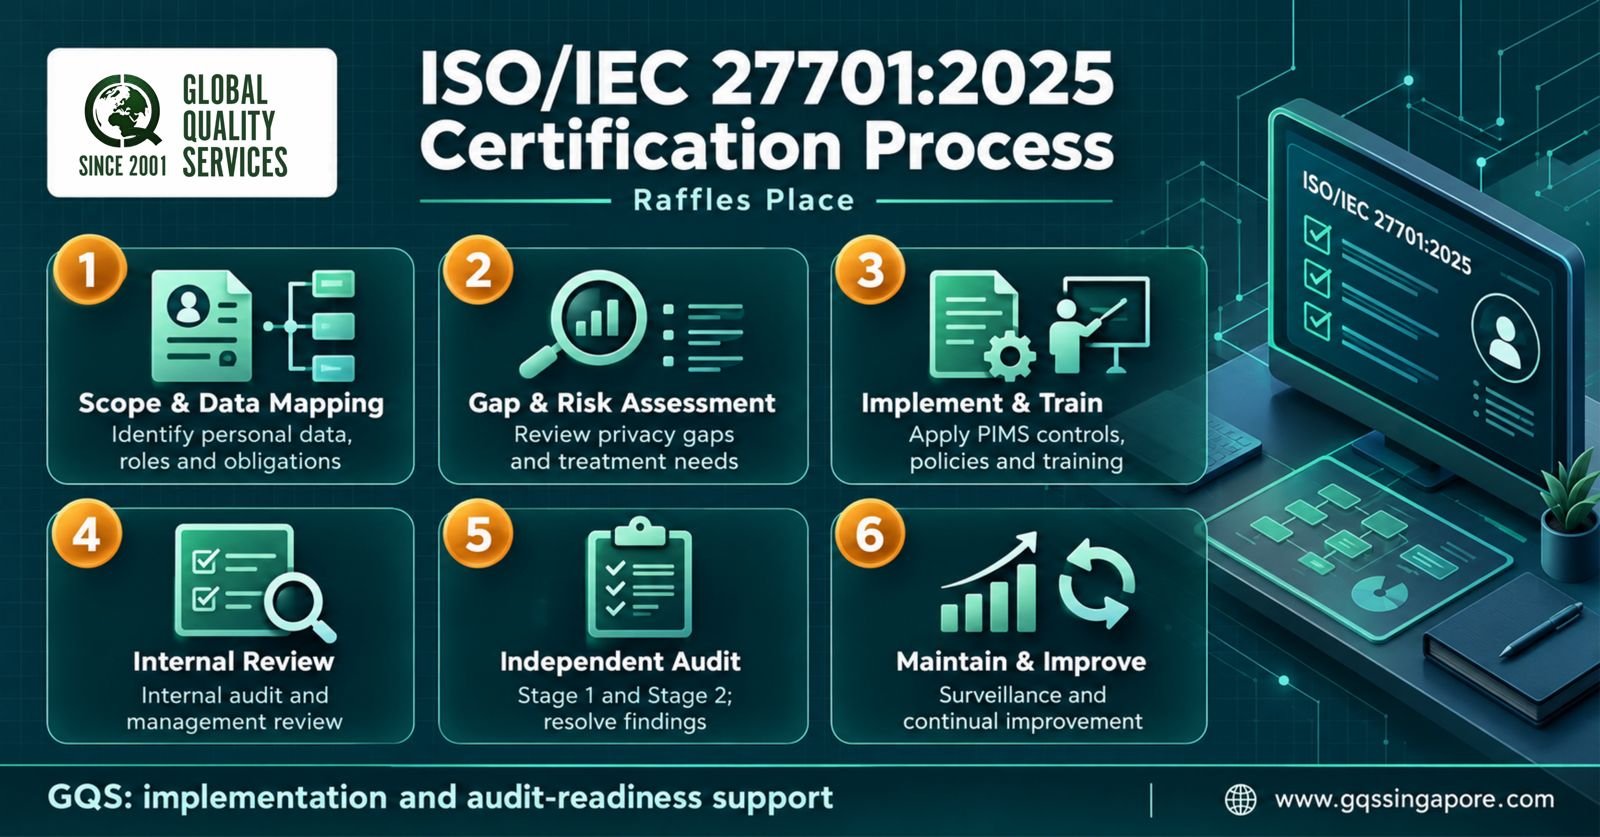
Global Quality Services follows a structured certification approach based on the agreed scope and applicable certification requirements.
1. Define the Certification Scope
The organization identifies the business units, services, locations, information systems, and personal data processing activities to be included in the assessment. The scope should accurately reflect its role as a personal information controller, processor or both.
2. Review Privacy Management Arrangements
The organization’s documented policies, risk assessments, privacy responsibilities, operational control,s and supporting records are evaluated against the applicable standard requirements.
3. Conduct the Certification Audit
An audit is conducted to evaluate whether the Privacy Information Management System meets the relevant requirements. The assessment considers documented processes and objective evidence of how the system operates within the agreed scope.
4. Address Nonconformities
Where nonconformities are identifiedthe organizationnn must undertake appropriate corrective action and provide the required evidence for review in accordance with the certification process.
5. Certification Decision and Ongoing Requirements
Certification is granted only after the applicable audit requirements have been satisfied and the certification decision has been completed. Ongoing surveillance or other follow-up activities are determined by the applicable certification scheme and contractual arrangements.
ISO/IEC 27701:2025 and Singapore’s PDPA
Organizations seeking ISO/IEC 27701:2025 Certification in Raffles Place should understand the relationship between an international privacy management standard and Singapore’s data protection legislation.
The PDPA governs how organizations within its scope collect, use, and disclose personal data, subject to its applicable provisions and exceptions. The law also includes requirements for protection, retention, access and correction, and overseas transfers of personal data.
ISO/IEC 27701:2025 provides a management system framework for establishing, maintaining and continually improving privacy practices. It can help organizations organize their processes and demonstrate accountability, but it is not a substitute for a legal assessment of their obligations under the PDPA.
Businesses operating internationally may also need to consider the privacy laws applicable in the countries where they operate or process personal information.
ISO/IEC 27701:2019 vs ISO/IEC 27701:2025
Organizations with an existing ISO/IEC 27701:2019 Privacy Information Management System should review their certification arrangements in light of the revised standard.
The 2019 edition was withdrawn on 14 October 2025, when the 2025 edition was published. The newer edition is a standalone management system standard, not an extension that depends on ISO/IEC 27001 certification.
Organizations should therefore assess the 2025 edition’s requirements, identify changes affecting their current privacy management arrangements, and confirm the applicable transition or recertification requirements with their certification provider.
An existing ISO/IEC 27001 certificate may remain relevant to information security management, but it does not automatically establish conformity with ISO/IEC 27701:2025.
Why Choose Global Quality Services for ISO/IEC 27701:2025 Certification in Raffles Place?
Global Quality Services offers certification services for organizations seeking to establish confidence in their management systems and demonstrate conformity with applicable international standards.
For businesses in Raffles Place, the certification engagement is based on the organization’s activities, the agreed audit scope, and the requirements of ISO/IEC 27701:2025.
Organizations can discuss their current privacy management arrangements, existing certifications, business requirements, and intended certification scope with Global Quality Services before proceeding with the certification process.
Contact Global Quality Services to discuss ISO/IEC 27701:2025 Certification in Raffles Place, Singapore, and determine the appropriate certification scope for your organization.
Frequently Asked Questions
1. Can a company in Raffles Place apply for ISO/IEC 27701:2025 certification if its data is hosted overseas?
Yes. Overseas data hosting does not automatically prevent an organization from pursuing certification. The assessment scope should account for relevant data flows, certification providers, processing responsibilities, contractual arrangements, and applicable privacy requirements. Overseas transfers must also be evaluated against the laws that apply to the organization.
2. Is ISO/IEC 27701:2025 certification mandatory for businesses in Singapore?
ISO/IEC 27701:2025 certification is not a blanket legal requirement for every Singapore business. However, a customer, business partner, procurement process, or contractual arrangement may require or prefer it. Organizations should distinguish between voluntary certification and their statutory obligations under Singapore’s PDPA and Certificationble laws.
3. Can a small business or startup in Raffles Place obtain ISO/IEC 27701:2025 certification?
Yes. The standard applies to organizations of all sizes, including small businesses and startups. The certification scope should match the organization’s activities and accurately cover the personal information it controls or processes. Smaller organizations should establish appropriate documented processes and objective evidence rather than assume that their size exempts them from the standard’s requirements.
4. Does ISO/IEC 27701:2025 certification cover GDPR requirements for European customers?
The standard provides a privacy management framework that can support an organization’s approach to GDPR-related responsibilities. However, certification does not automatically establish full GDPR compliance or remove the need to evaluate requirements such as lawful processing, data subject rights, international data transfers, and other applicable obligations.
5. How can we verify whether an ISO/IEC 27701:2025 certificate is valid?
Request the certificate and check the issuing certification body’s identity, theorganization’ss legal name, the applicable standard and edition, the certified scope, issue and expiry details, and the certificate’s current status. Where applicable, verify the certification body’s accreditation and confirm the certificate directly with the issuing body or its official certificate directory. An accreditation claim should be checked against the relevant accreditation body’s records.