Many businesses based in One-North focus on technology, innovation research, new company startups, and digital product development. These types of companies often deal with sensitive information, design software applications, and operate on connected networks that provide services to their consumers. In other words, cyber risks are imminent for One-North businesses, and one wrong click or even exposure of passwords and systems could result in loss of important data and dissatisfied clients.
According to the report released by the CSA in 2025, 284,300 infected systems were identified in Singapore; this number is 142% higher compared to 2024. It only proves the importance of monitoring the situation regarding cybersecurity risks and evaluating current protective measures adopted by organizations.
As part of our service portfolio, Global Quality Services supports companies operating in One-North in assessing their cybersecurity management approaches and identifying gaps in the framework. With our ISO 27032 consultancy solutions, businesses will have a chance to improve their information protection strategies and client interactions.
What Is ISO 27032 and Why Does It Matter for One-North Businesses
The ISO/IEC 27032 standard offers best practice guidance related to cybersecurity risk management and the associated challenges inherent in the usage of the Internet and interconnecting systems. The framework gives businesses a comprehensive understanding of the relationship between several aspects of cybersecurity such as network security, information security, and Internet security.
The guidance is especially valuable to firms operating within One-North. Companies with cloud computing, digital platforms, external vendors, and remote access to corporate networks can leverage the standard to improve their risk management processes. The support will allow your firm to achieve improved outcomes regarding:
- Identifying and managing cybersecurity risks
- Reducing the risk of phishing, malware, and unauthorized access
- Setting clear security responsibilities across teams
- Improving cyber incident reporting and response
- Sharing security information with relevant stakeholders
- Helping employees recognize and report online threats
ISO/IEC 27032 is a guideline cybersecurity standard, whereas ISO/IEC 27001 is a certifiable management systems standard. Companies tend to look for ISO 27032 certifications despite the fact that no such certificates exist, since certificate offerings differ based on scheme and issuer.
Why One-North Companies Should Consider ISO 27032 Certification
Even the simplest events could trigger a cybersecurity incident, such as clicking on a malicious link or outsourcing work to providers who use inadequate security controls.
Without a good understanding of how to respond to such incidents, minor events will rapidly snowball into disruptions to your organization’s processes. ISO 27032 certification involves reviewing your risks to assess areas requiring improvement in your security practices.
Protect Business and Customer Information
Your company could have customer databases, research results, product designs, financial data, or other proprietary files. Should any unauthorized individual get their hands on such information, there will probably be negative repercussions that extend far beyond whatever initial harm was done. It might be wise to conduct a thorough examination of your cybersecurity procedures.
Prepare Your Team to Handle Cyber Incidents
Clear incident response procedures help employees report security threats quickly, follow the right steps, and limit potential damage. This reduces confusion during an incident and helps your business restore normal operations sooner.
Build Trust with Clients and Business Partners
A client will most likely ask about your data security practices before they sign any contract with you. This is where having established procedures regarding cybersecurity comes into play. While these procedures won’t ensure a breach won’t ever occur, at least you’ll be able to prove you take your obligations very seriously.
Manage Risks Across Connected Systems
Security doesn’t only revolve around the technology deployed within your organization’s walls. Your vulnerability to cyber risks may be impacted by cloud providers, third-party applications, contractors, and other outside vendors too. You can apply ISO 27032 principles to assess these dependencies and evaluate whether your existing controls are sufficient based on your operations and needs.w
Support Your Wider Information Security Goals
If your business also needs a formal information security management system, ISO 27001 Certification in Singapore may be worth considering. The right choice depends on your business needs, client expectations, and existing security arrangements.
Who Needs ISO 27032 Certification in One-North
Here is the list of businesses that need ISO 27032 certification support:
- Technology startups
- Software development companies
- Research and innovation centers
- SaaS and cloud service providers
- Fintech and digital payment businesses
- Healthcare technology companies
- IT consulting and managed service providers
- Professional and corporate service firms
How Global Quality Services Experts Help You with ISO 27032 Certification in One-North
Selecting an ISO consultant involves much more than preparing documentation for assessment purposes. You require a specialist who understands your organizational requirements, advises you on areas that require improvement, and assists your team in implementing appropriate practices.
Global Quality Services provides consultancy services, including ISO certification consulting, implementation of management systems, training, and documentation preparation to companies within various sectors. Their expertise in different international standards enables them to advise businesses about their specific requirements.
Unlike generic consultants who provide uniform advice to all clients, reputable firms such as Global Quality Services prioritize customized solutions suited to your business.
Why Choose Global Quality Services
- More than 26 years of management consultancy experience
- Experience supporting businesses across different industries and markets
- Consultancy covering information security and other ISO management system standards
- Recommendations tailored to business size, operations, and security needs
Global Quality Services can also help you understand how cybersecurity fits into your wider information security and risk management plans.
Our ISO 27032 Certification Services in One-North
Your requirements may vary based on your current safety measures and risk profile. Global Quality Services can assist you with auditing your current setup, pinpointing any weaknesses, and recommending adjustments where necessary.
Cybersecurity Gap Assessment
Before making changes, you need to know where your current practices fall short. We review your existing cybersecurity controls, policies, procedures, and records to identify areas that need attention. This gives your team a clearer starting point and helps you focus on the most relevant issues.
Cybersecurity Policy and Documentation Support
Your employees need clear guidance on how to handle company information and respond to security concerns. We help you develop or improve relevant policies, procedures, assigned responsibilities, and supporting records.
The documents are prepared according to the agreed scope and the way your organization operates.
Risk Assessment and Control Guidance
Every business faces different cyber risks. We help you identify possible threats, consider their impact, and review the controls needed to manage them.
The recommendations take your systems, information assets, business activities, and existing security measures into account.
Employee Awareness and Training
Employees can help prevent many common security incidents when they know what to look for. We provide training support to help staff recognize suspicious emails, handle information carefully, follow company procedures, and report potential threats.
Internal Audit and Assessment Preparation
Before an external assessment, it helps to review whether your agreed controls are in place and whether the supporting records are available. We help you identify outstanding issues, review evidence, and prepare for the applicable assessment where required.
Our Approach to ISO 27032 Certification
Here is a complete process to achieve ISO 27032 certification:
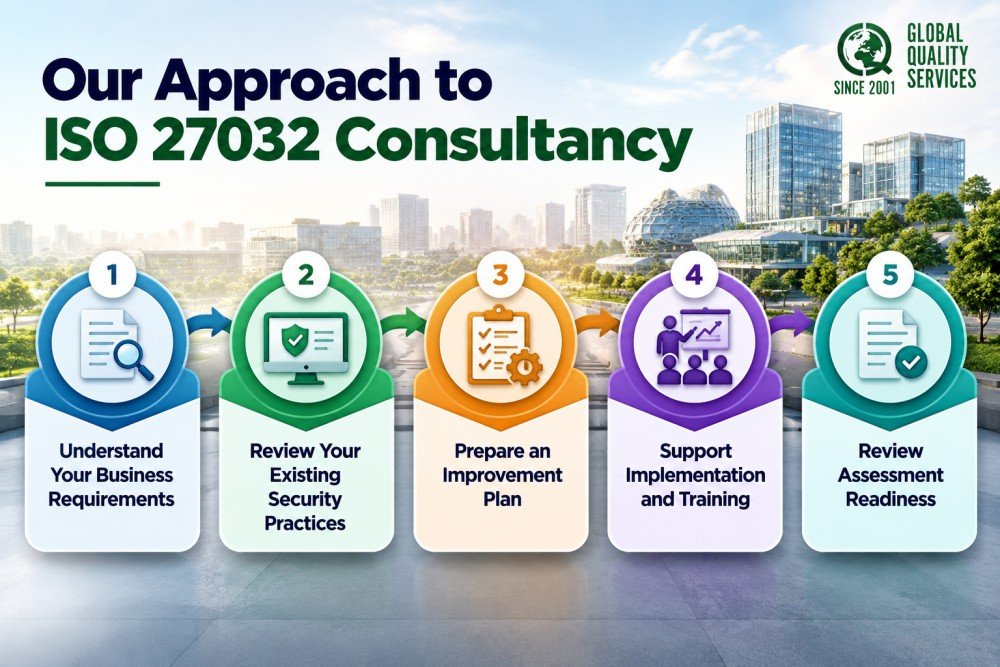
Step 1: Understand Your Business Requirements
We discuss your business activities, information assets, technology environment, client expectations, and current cybersecurity concerns. This helps define the scope of consultancy.
Step 2: Review Your Existing Security Practices
We examine available policies, risk assessments, procedures, and security controls to identify weaknesses and areas that need improvement.
Step 3: Prepare an Improvement Plan
We help your team set priorities, assign responsibilities, and develop the documentation needed for the agreed consultancy scope.
Step 4: Support Implementation and Training
We guide your team as it applies the agreed security practices, addresses identified gaps, and improves employee awareness.
Step 5: Review Assessment Readiness
We check the available evidence, review outstanding actions, and help your organization prepare for the applicable assessment or certification route.
Documents Required for ISO 27032 Consultancy
You do not need to prepare every document before contacting a consultant. However, having your existing records available can make the initial review easier. Depending on your business and the agreed scope, you may need:
- Company profile and details of business activities
- Existing cybersecurity policies and procedures
- Information asset inventory
- Cybersecurity risk assessments and risk registers
- Network and system security records
- User access management procedures
- Incident response and reporting procedures
- Employee cybersecurity training records
- Third-party and supplier security records, where applicable
- Internal audit findings and corrective action records, if available
How Much Does ISO 27032 Consultancy Cost in One-North
One thing to note is that one fee does not apply to everyone. For example, ISO 27032 consulting costs in One-North vary according to organizational size, number of systems, current security procedures, and level of support needed.
Organizations already having cybersecurity guidelines will likely require fewer consultations compared to those who have none in place yet. Additional factors influencing cost include document creation, employee training sessions, setup help, and third-party assessments.
2At Global Quality Services, we conduct evaluations of needs followed by generation of quotes customized specifically to your circumstances. You’ll know what services will be provided and the price tag attached beforehand.
Get ISO 27032 Consultancy Support in One-North from Global Quality Services
Your business should not have to wait for a security incident to find weaknesses in its systems and procedures. A timely review can help you understand where your current practices need attention and what you can do to improve them.
Global Quality Services works with businesses to review cybersecurity gaps, improve documentation, and prepare for relevant assessments based on their operational needs.
Visit our contact page or call +65 9344 1973 to speak with our Singapore team. Tell us about your business, existing security arrangements, and compliance goals. Our team will help you understand the suitable consultancy scope, available assessment options, and the next steps for your organization.
Frequently Asked Questions
1. What Is ISO 27032 Certification?
ISO/IEC 27032 provides guidelines for cybersecurity, including risks involving connected systems, online activities, and information shared across digital environments. It is not a standalone certifiable management system standard. Any certificate offered under a related scheme should be checked against the scheme’s requirements and the issuing organization’s authority.
2. Can Businesses in One-North Apply for ISO 27032 Consultancy?
Yes. Startups, software companies, research organizations, cloud service providers, and other businesses in One-North can seek consultancy to review cyber risks, improve security practices, and prepare the relevant documentation.
3. How Long Does ISO 27032 Consultancy Take?
The timeline depends on your company’s size, current security arrangements, available documentation, and the scope of consultancy. A consultant can provide a more useful estimate after reviewing your requirements.
4. Is ISO 27032 the Same as ISO 27001?
No. ISO/IEC 27032 provides cybersecurity guidance. ISO/IEC 27001 sets out requirements for an information security management system that can be certified by an appropriate certification body. Businesses may use the two standards to support different but related security objectives.
5. What Are the Benefits of ISO 27032 Consultancy?
Consultancy can help your business identify security weaknesses, improve employee awareness, strengthen incident response procedures, clarify responsibilities, and prepare supporting records. The results depend on how well your organization puts the recommendations into practice.