Marina Bay is a major business and financial center in Singapore, home to fintech companies, financial institutions, technology firms, and regional businesses.
Singapore’s digital economy reached S$144.1 billion in 2025, contributing 19.3% of GDP. Enterprise AI adoption also increased to 23.5%, highlighting the growing importance of secure digital operations.
SOC 2 Type 2 in Marina Bay helps service organizations demonstrate that relevant security and operational controls are designed appropriately and operated effectively over a defined period.
What Is SOC 2 Type 2?
SOC 2 Type 2 certification is an AICPA reporting framework based on the Trust Services Criteria: Security, Availability, Processing Integrity, Confidentiality, and Privacy.
A Type 2 examination evaluates whether relevant controls are suitably designed and operating effectively over a defined period.
Unlike Type 1, which assesses controls at a specific point in time, Type 2 provides evidence of ongoing control operation. SOC 2 Type 2 is technically an independent attestation report, rather than an ISO-style certification.
An independent service auditor or CPA firm performs the examination and issues the report. A consultancy can provide readiness and preparation support but does not issue the independent SOC 2 report.
Why SOC 2 Matters for Businesses in Marina Bay
Marina Bay sits within Singapore’s wider financial and technology ecosystem, bringing together financial institutions, fintech companies, technology providers and regional businesses. Singapore now has more than 1,800 FinTech firms.
For businesses operating in this environment, security and technology controls can directly influence customer confidence, vendor relationships, and enterprise procurement decisions. SOC 2 Type 2 provides independent assurance that relevant controls are not only appropriately designed but also operating effectively over a defined period.
SOC 2 Type 2 and Singapore Compliance
SOC 2 can complement Singapore’s regulatory requirements but does not replace them.
PDPA
Singapore’s Personal Data Protection Act establishes obligations for organizations handling personal data. SOC 2 may assure relevant privacy and security controls, but it does not automatically demonstrate complete PDPA compliance.
MAS Requirements
Financial institutions and businesses serving the financial sector may also need to address MAS requirements covering technology risk, cyber hygiene, outsourcing and operational resilience.
SOC 2 can support vendor due diligence, but it does not replace applicable MAS requirements.
SOC 2 Type 2 and AI Security
AI adoption among Singapore enterprises reached 23.5% in 2025, according to IMDA. Singapore’s enhanced Cyber Trust framework also specifically addresses AI security.
Organizations using AI within their SOC 2 environment may need to review access controls, data protection, third-party AI services, monitoring, risk management, and change controls.
SOC 2 is not an AI certification, but organizations can address relevant AI risks within their broader control environment.
SOC 2 Compliance & Reporting Costs in Singapore
The investment required for SOC 2 compliance varies, influenced by several factors that determine the complexity and scope of the compliance process. Our experienced consultants will work closely with you to understand your unique requirements and provide a clear cost estimate, accounting for factors such as:
- Selected Trust Services Principles(TSPs)
- Organizational Size and Complexity
- Current Security Infrastructure
- Consulting and Advisory Services
- Training and Employee Awareness
- Documentation and Process Enhancements
- Internal Audits and Assessments
- Third-Party Assessment Fees
- Ongoing Monitoring and Maintenance
- Technology and Infrastructure Upgrades
- Miscellaneous Expenses
Approach SOC 2 compliance as a strategic investment in your organization’s security resilience. The benefits, including strengthened data protection, heightened client trust, and adherence to regulations, far outweigh the initial costs. Our dedicated consultants will provide a tailored cost estimation, ensuring transparency and alignment with your objectives.
Who Should Consider SOC 2 Type 2 in Marina Bay?
The following organizations must consider applying for SOC 2 Type 2 in the Marina Bay area:
Fintech and Financial Technology Companies
Fintech businesses handling financial information, customer data, or payment technology can use SOC 2 to demonstrate control effectiveness to enterprise customers and partners.
SaaS and Cloud Service Providers
SaaS and cloud companies often face security reviews before being approved as enterprise technology vendors. SOC 2 Type 2 can provide independent assurance over relevant controls.
Data and AI Companies
Organizations processing sensitive business data or deploying AI applications can use SOC 2 to strengthen assurance around access, security, monitoring, and information handling.
Technology Vendors
Technology providers serving banks, insurers, multinational companies, and other enterprise customers may benefit from SOC 2 as part of their vendor-assurance program.
Benefits of SOC 2 Type 2 Certification in Marina Bay
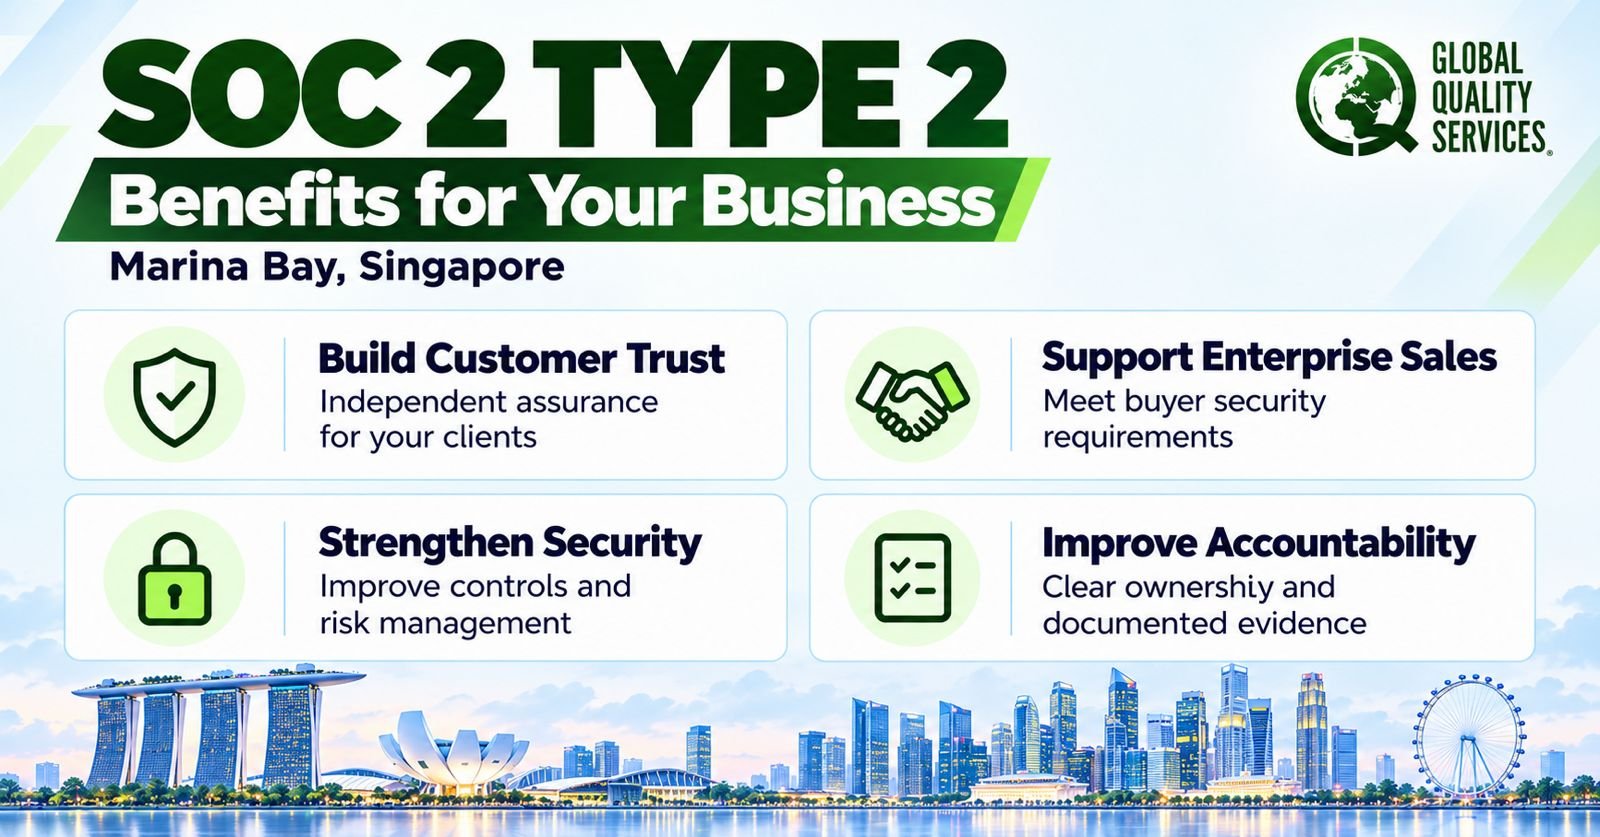
SOC 2 Type 2 provides independent assurance that an organisation’s controls are designed and operating effectively over a defined period. For technology, fintech, SaaS and data-driven businesses in Marina Bay, this can strengthen customer confidence and support third-party risk assessments.
Build Customer Trust
A SOC 2 Type 2 report gives customers and business partners greater visibility into how an organisation protects information and manages its technology environment. This can be particularly valuable when customers need assurance before sharing sensitive business or personal data.
Strengthen Information Security
The SOC 2 framework assesses controls relevant to security and, where selected, availability, processing integrity, confidentiality and privacy. The examination can help organisations identify control weaknesses and strengthen their overall security environment.
Support Fintech and Financial Services Relationships
Marina Bay has a strong financial technology ecosystem, with Singapore now home to more than 1,800 FinTech firms. A SOC 2 Type 2 report can help technology providers demonstrate their control environment when working with financial institutions and other security-conscious customers.
Improve Vendor and Third-Party Due Diligence
Businesses increasingly need evidence that their technology and service providers manage security and operational risks effectively. SOC 2 Type 2 documentation can provide useful assurance during vendor assessments, procurement reviews and customer security questionnaires.
Support Cross-Border Business
Singapore businesses often serve customers and partners across multiple markets. A recognised SOC 2 Type 2 report can provide a structured way to communicate the effectiveness of relevant controls to international customers and business partners.
Create Stronger Operational Discipline
Preparing for a Type 2 examination requires organisations to consistently operate and retain evidence of their controls over an examination period. This encourages stronger processes for access management, incident response, risk management, monitoring and other control activities.
Complement Singapore Compliance Efforts
SOC 2 Type 2 does not replace Singapore regulatory requirements such as the PDPA or MAS requirements. However, the control evidence developed through a SOC 2 programme can support an organisation’s broader approach to information security, privacy and technology risk management.
What Does SOC 2 Type 2 Cover?
The scope depends on the organization’s services and selected Trust Services Criteria.
Security
Controls can cover access management, authentication, security monitoring, vulnerability management, incident response and change management.
Availability
Where applicable, controls can address system monitoring, backup, disaster recovery, capacity management and business continuity.
Processing Integrity
This focuses on whether system processing is complete, accurate, timely, valid and authorized.
Confidentiality
Controls help protect information identified as confidential from unauthorized access, disclosure or use.
Privacy
Where included, Privacy controls address the collection, use, retention, disclosure and disposal of personal information.
SOC 2 Type 2 Readiness Checklist
Before an examination, organizations should confirm that their scope is clearly defined and that they have identified the relevant Trust Services Criteria.
Organizations should implement security and access controls, ensure control owners understand their responsibilities, and establish processes for managing risks, incidents, changes, and vendors.
Organizations should also maintain reliable evidence that controls operate consistently. A readiness assessment can identify gaps before the independent examination begins.
SOC 2 Type 2 Examination Process in Marina Bay
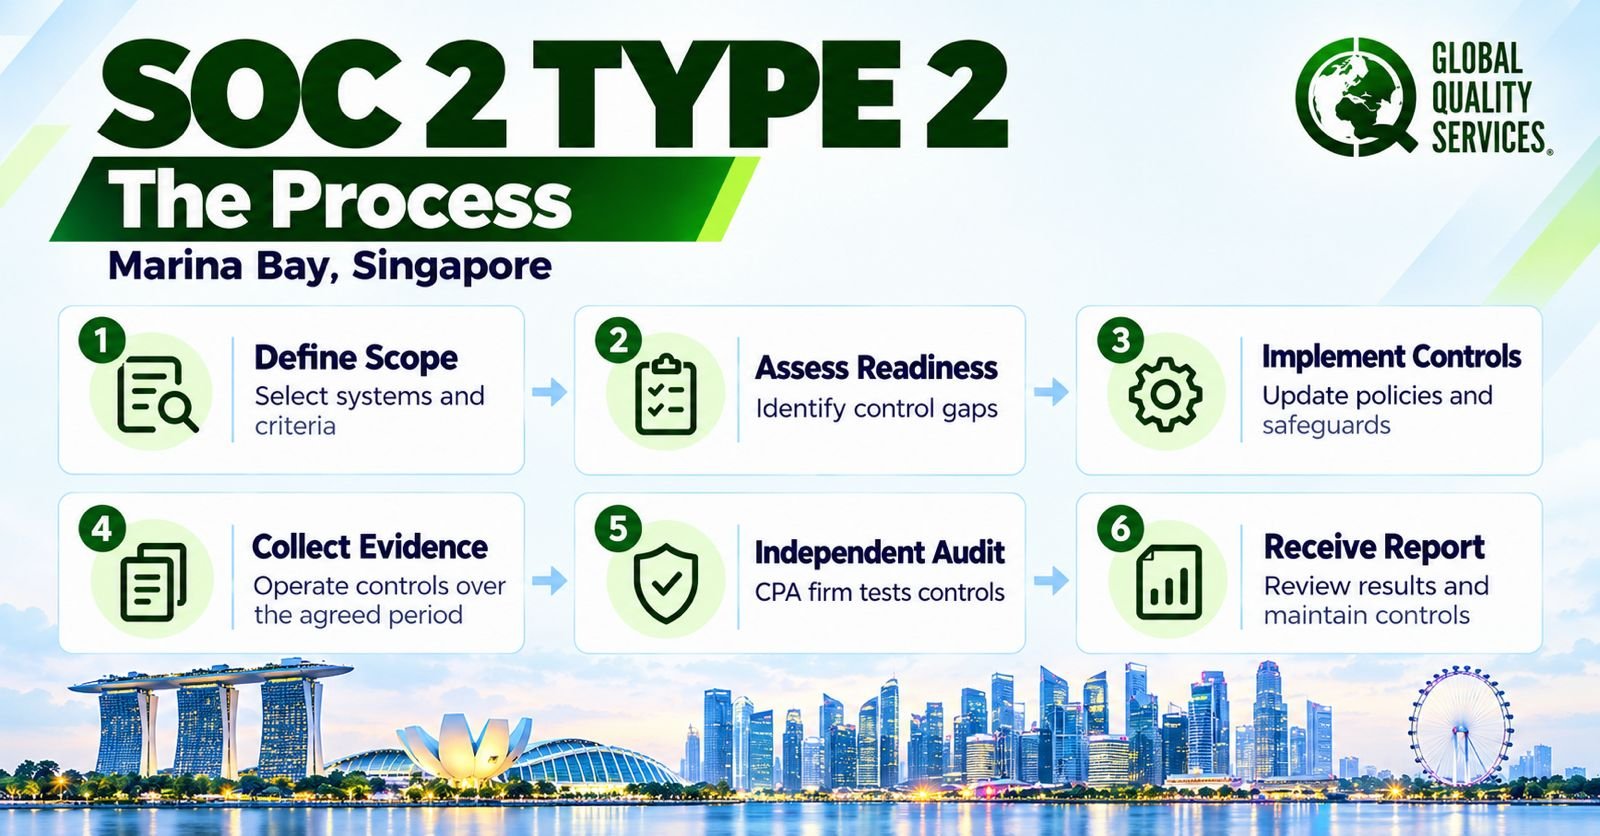
1. Define the Scope
Identify the services, systems, applications, and processes included in the examination.
2. Select the Criteria
Determine which Trust Services Criteria apply to the organization’s services and customer commitments.
3. Conduct a Gap Assessment
Review existing controls and identify areas requiring improvement.
4. Strengthen Controls
Address identified gaps and establish appropriate security, access, monitoring, and operational controls.
5. Collect Evidence
Establish processes for maintaining evidence throughout the examination period.
6. Complete the Independent Examination
The independent service auditor evaluates the relevant controls and their operating effectiveness.
7. Receive the Report
The service auditor issues the SOC 2 Type 2 report after completing the examination.
How Can GQS Help With SOC 2 Type 2 in Marina Bay?
Global Quality Services can support organizations with SOC 2 Type 2 readiness, gap assessment, control documentation, implementation support, evidence preparation,n and examination readiness.
GQS can also help organizations understand how their SOC 2 control environment can work alongside Singapore requirements such as the PDPA, MAS expectations and the Cyber Trust framework.
The independent service auditor remains responsible for the formal SOC 2 examination.
Frequently Asked Questions
Is SOC 2 Type 2 mandatory in Singapore?
No. It is not a general legal requirement, although customers, enterprise buyers, or business partners may require it.
Is SOC 2 Type II recognized as an ISO/IEC 27001 equivalent in Singapore?
No. CSA currently recognizes ISO/IEC 27001 as the relevant equivalent for the Cyber Trust Mark, not SOC 2 Type II.
Does SOC 2 Type 2 prove PDPA compliance?
No. SOC 2 can support relevant security and privacy controls but does not automatically demonstrate full PDPA compliance.
Can fintech companies in Marina Bay benefit from SOC 2?
Yes. SOC 2 can provide independent assurance that supports enterprise customer and vendor due diligence.
Who issues the SOC 2 Type 2 report?
An independent qualified service auditor or CPA firm performs the examination and issues the report.